VulnApproval

Suppression Approval · NIS2 Compliance

Accepted risk, formally signed.

Turn a vulnerability suppression into a CIO-approved, digitally signed risk acceptance — a NIS2 Exception Policy with a unique ID, audit-ready.

THE PROBLEM

A suppression without signature is a compliance gap.

In normal operations, some vulnerabilities are temporarily suppressed at the request of server owners. However, the NIS2 Directive (Art. 21) requires each accepted risk to be documented and formally approved by management.

A suppression without CIO approval is a compliance gap — and a concrete risk during NIS2 or ISO 27001 audits.

HOW IT WORKS

From suppression to signed Exception Policy.

VulnApproval is the SaaS system managed by Cyberfero that extracts suppressions from any supported VM system, enriches each record with the server owner from ServiceNow CMDB, composes a package in management language for the Global CIO, and collects the digital signature — issuing a formal NIS2 Exception Policy (EP-XXX) as auditable evidence.

Badge: SaaS · NIS2 · Multitenant · Multilingual IT/EN

One platform, every VM system, every legal entity.

VM System agnostic — 8 platforms

The VM connector is configurable per tenant and replaceable without impact on the approval flow, documents, or audit trail. Switch Vulnerability Management platforms by updating only the connector configuration.

Platform features

VM System agnostic

8 platforms with a common interface. Switch VM systems without touching the approval flow or audit trail.

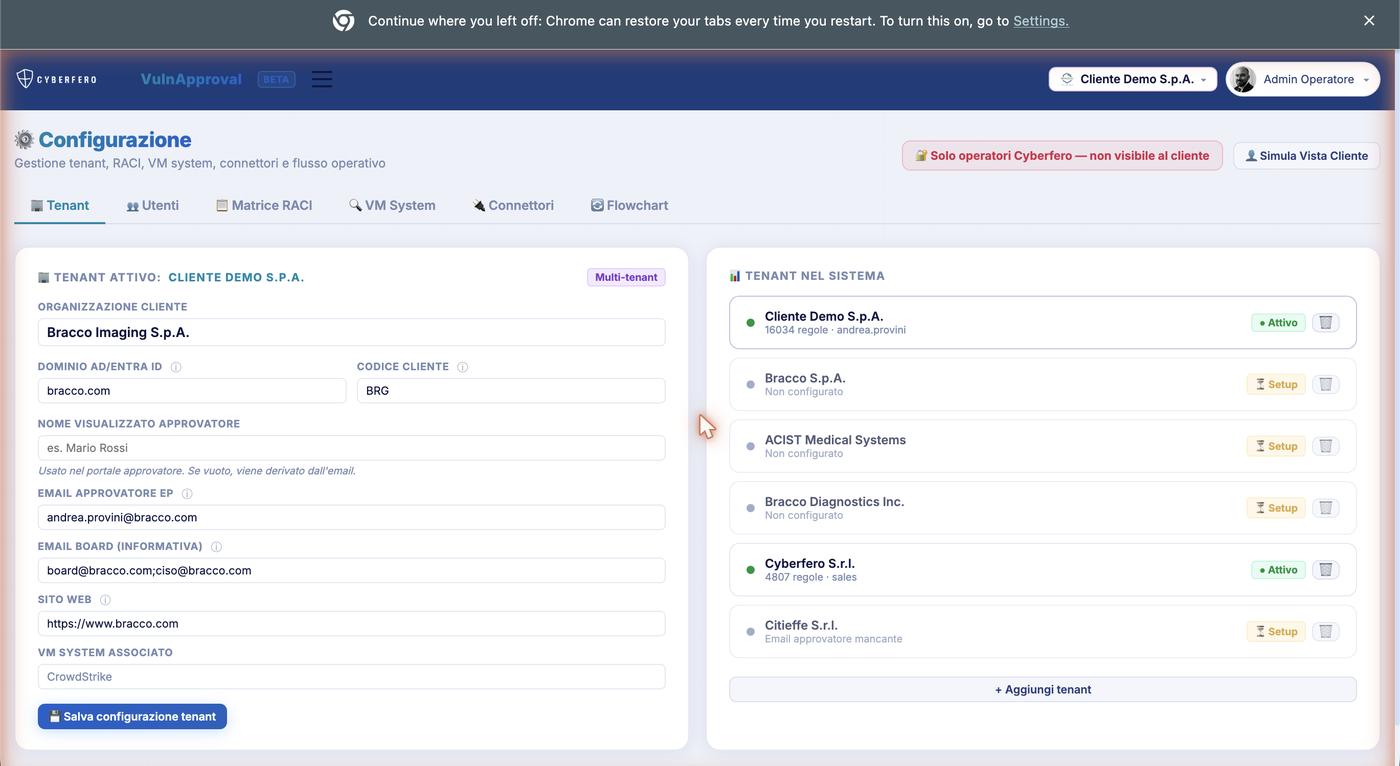
Multitenant architecture

A single platform manages all the group's legal entities with isolated data, encrypted credentials and an independent flow.

ServiceNow CMDB

Automatic enrichment of the server owner from the u_server_owner field. No manual search for the owner.

NIS2 Exception Policy

EP-YYYY-TTT-NNN document with unique ID, scope, compensating measures, and validity — ready evidence for NIS2 and ISO 27001 audits.

Flexible digital signature

Mode A via API (DocuSign, Adobe Sign, Namirial) or Mode B manual upload. Both modes coexist and are selectable after go-live.

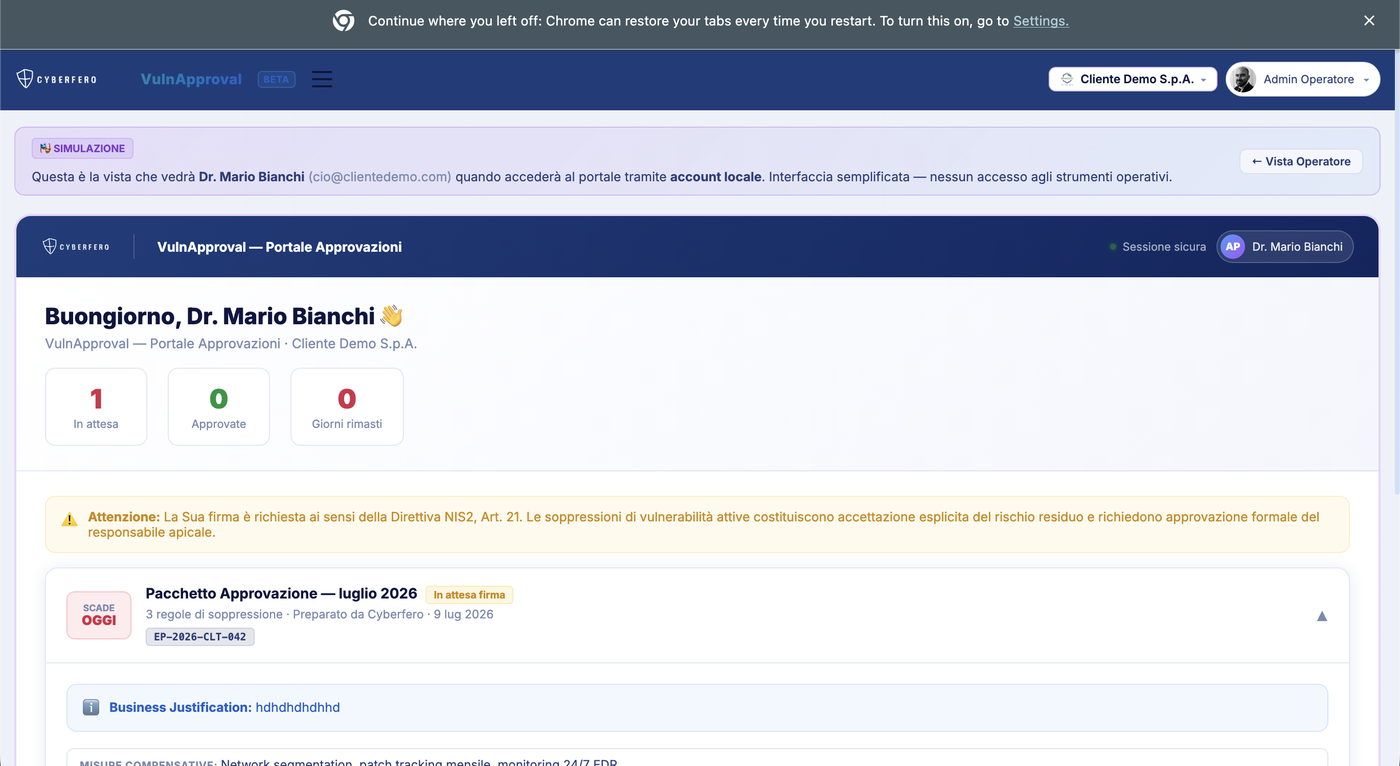
Dedicated CIO portal

The CIO signs or rejects with one click. If rejected, the suppression is automatically deleted via API in the VM system within seconds.

Immutable audit trail

Immutable 5-year retention, SHA-256 hash, automatic pre-expiry reminders: evidence ready for any inspection.

Periodic synchronization

Automatic pull every 6 hours with mark-and-sweep: expired or removed suppressions updated in real time.

Entra ID SSO

Microsoft Entra ID (OIDC) authentication for client tenant users, with native MFA and Conditional Access.

Security included in the subscription

TLS 1.3 + LUKS

Encryption in transit (TLS 1.3) and at rest (LUKS filesystem). Data always protected.

Tenant isolation

Cryptographically separated data per tenant. VM and CMDB credentials in a Fernet-encrypted vault.

Backup & SLA 99.5%

RPO 24h · RTO 4h · European data center. Cyberfero manages infrastructure and monitoring.

Process-aligned, not a generic GRC tool.

No commercial solution natively integrates multiple VM systems, management approval workflow, CMDB ownership, and flexible signing in a single NIS2 flow.

VM System agnostic

The VM connector is configurable per tenant and replaceable without impact on the flow. Switch platforms by updating only the configuration.

CMDB-based ownership

Automatic enrichment from ServiceNow: every suppression has its real owner, without manual lookup in the corporate CMDB.

Formal Exception Policy

EP-XXX document with unique ID, scope, compensating measures, and validity — ready evidence for NIS2 and ISO 27001 audits.

Flexible signature

Mode A (DocuSign, Adobe Sign, Namirial) and Mode B (manual upload) coexist — selectable even after go-live, without migrations.

Automatic rejection

If the CIO rejects, the suppression is automatically deleted via API in the VM system: the vulnerability becomes visible again within seconds.

Secure multitenant

Cryptographically isolated data per tenant, credentials encrypted in a separate vault, independent logical schema for each legal entity.

MSSP expertise

Ten years of cybersecurity expertise: Cyberfero knows the real vulnerability management processes of enterprise companies.

REMEDIA + VulnApproval: governance end-to-end.

VulnApproval closes the remediation loop: when a vulnerability cannot be fixed in time, it governs formal risk acceptance up to executive sign-off. One asset model, one Entra ID SSO, one audit trail.

Detection → Remediation → Suppression → CIO Approval → EP NIS2

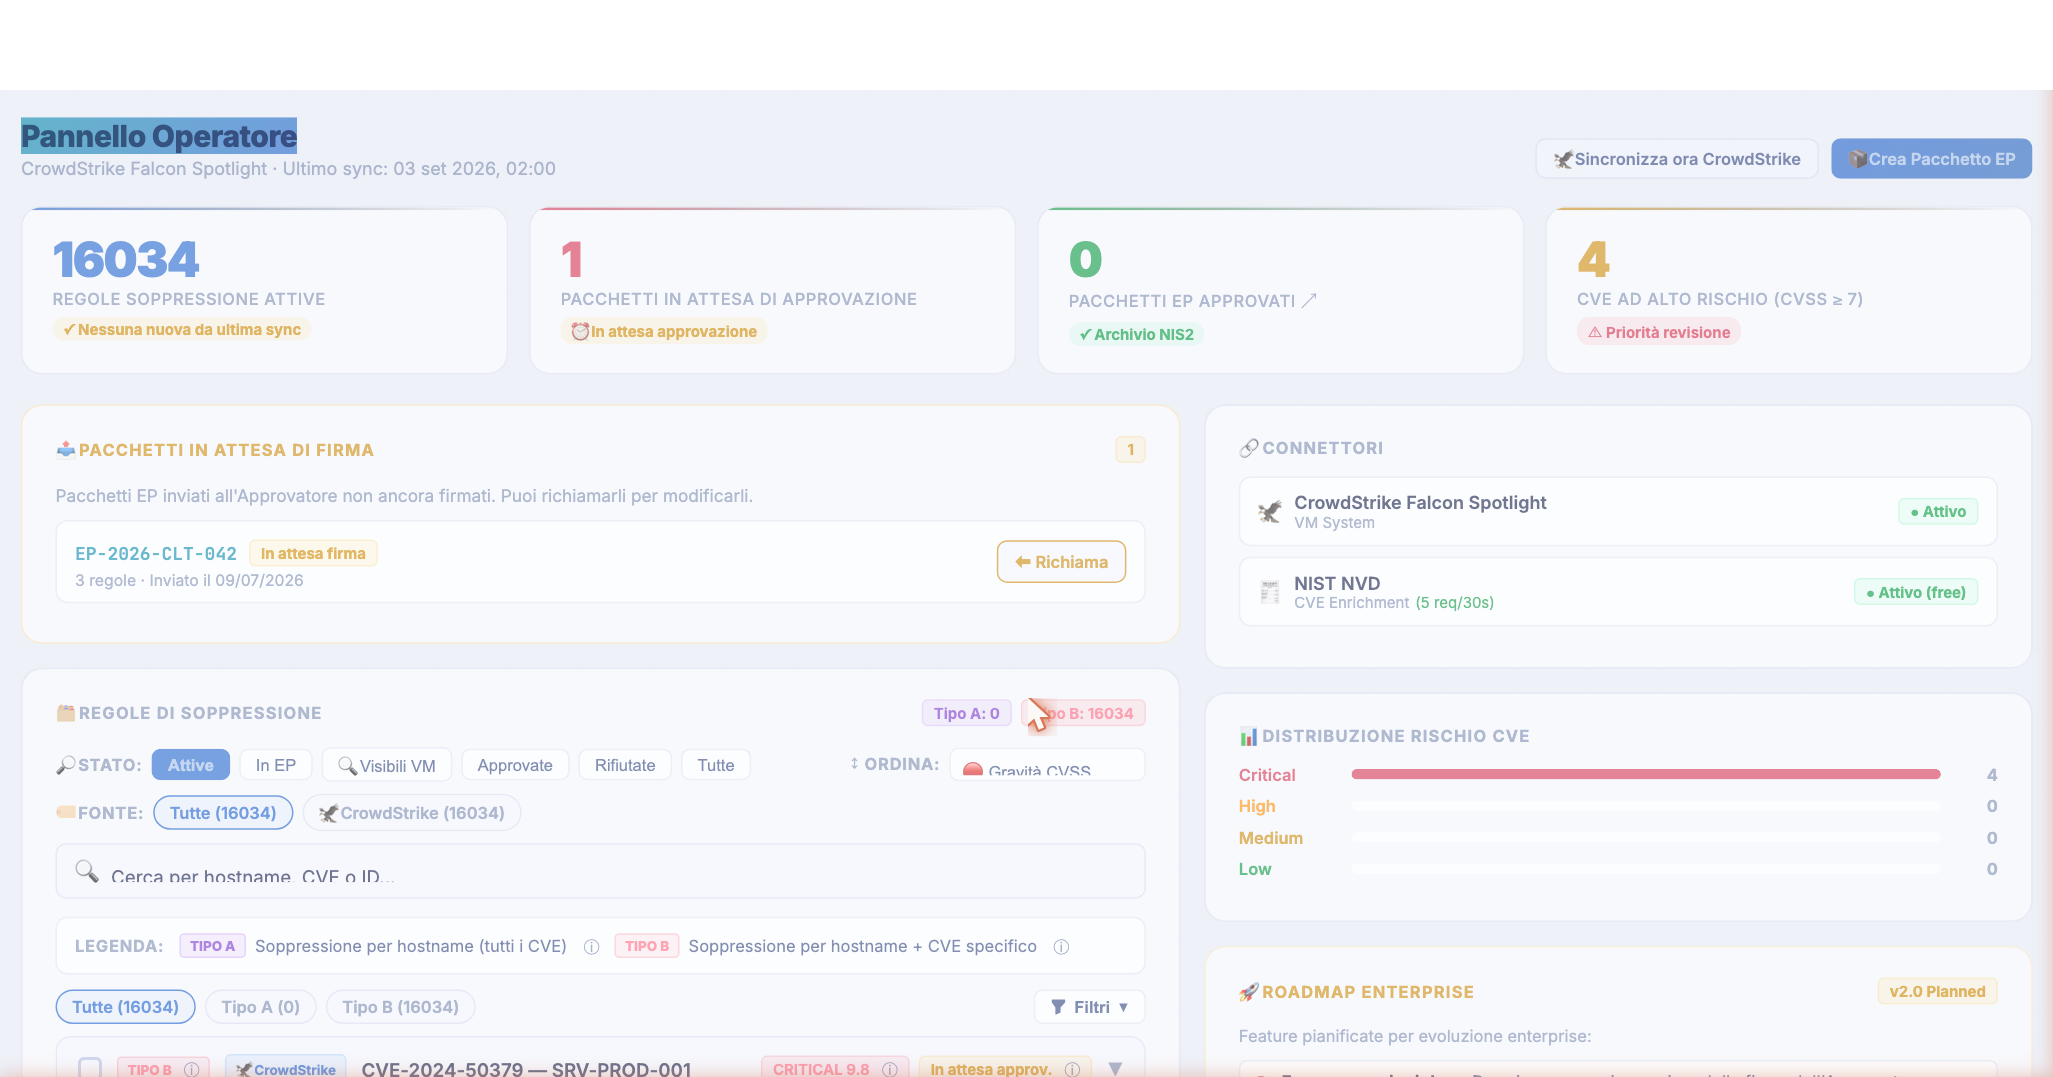
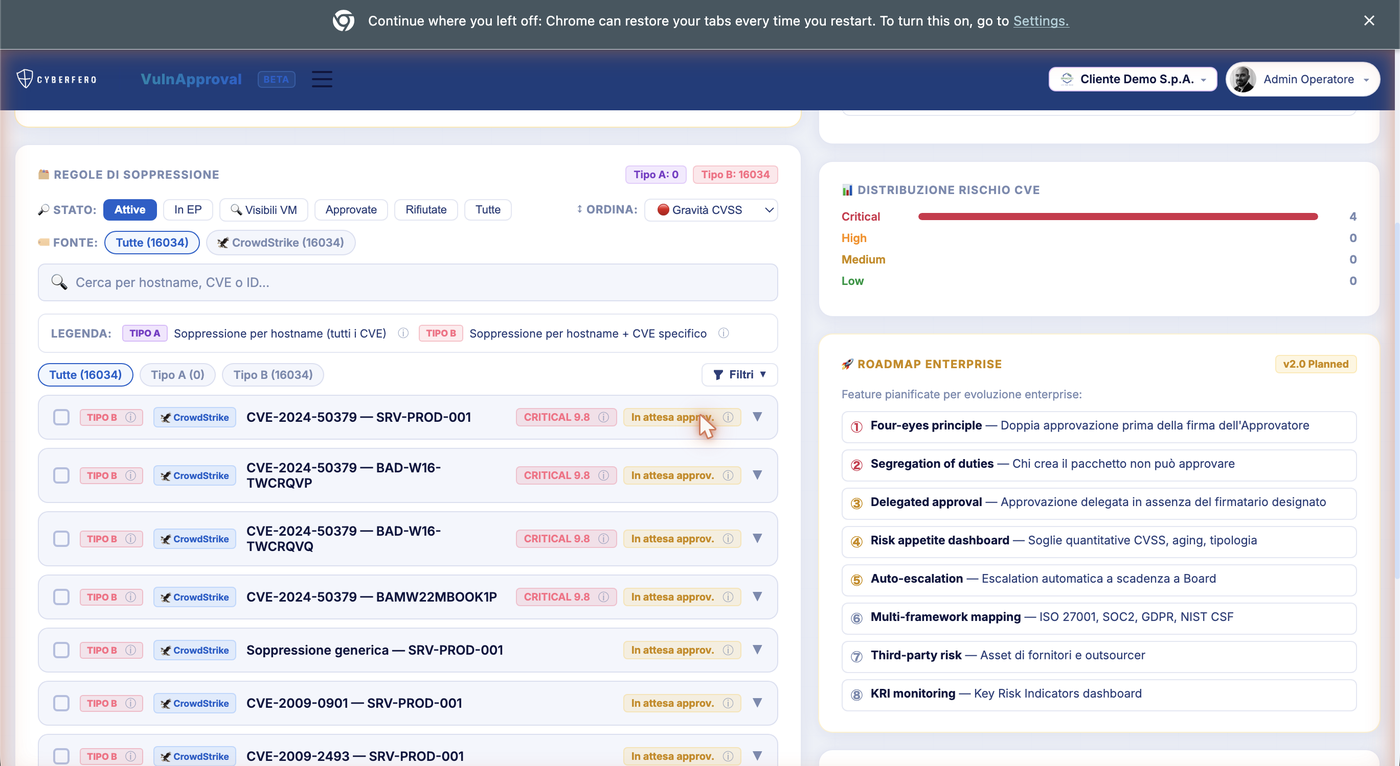
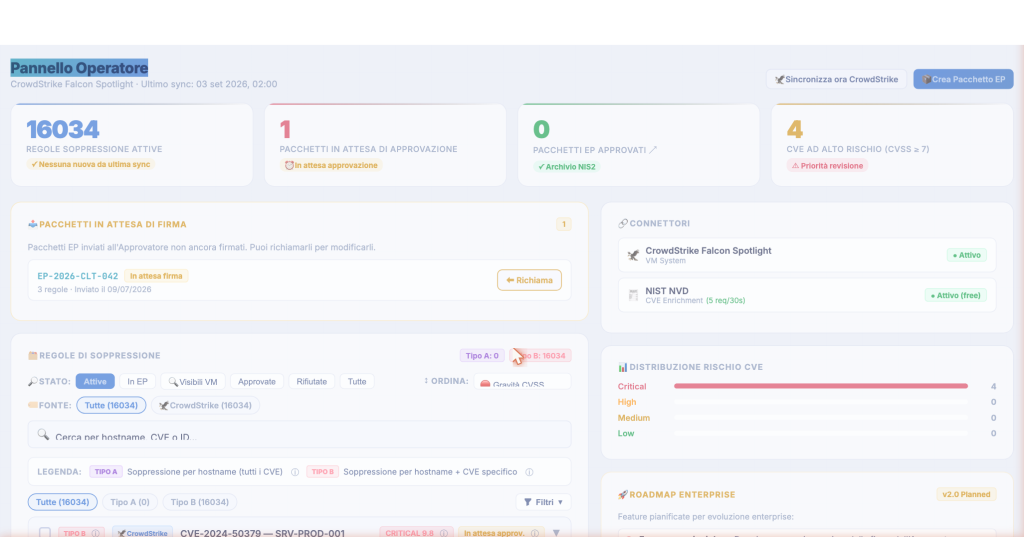
VulnApproval pannello operatore con lista soppressioni attive

Frequently asked questions

Does VulnApproval replace my Vulnerability Management system?

No. VulnApproval is not a VM system — it connects to the one you already use (CrowdStrike, Tenable, ConnectSecure, etc.) and adds the formal NIS2 approval flow for suppressions. Your VM system continues to detect vulnerabilities as before.

How does the connection to the VM system work?

Via tenant-configurable native connectors. Enter the API credentials in settings, click ‘Test connection’, and the system starts syncing. No on-premise installation required.

Does the data remain in Europe?

Yes. The infrastructure is managed by Cyberfero in European data centers with LUKS filesystem encryption and TLS 1.3. Each tenant has cryptographically separated data.

Is VulnApproval suitable for groups with multiple legal entities?

Yes, it is designed for this. The multitenant architecture manages all group legal entities from a single interface, each with its own approval flow, EP numbering, and signing CIO.

Is it possible to get a demo?

Yes. Contact us via the form below: we will arrange a personalised demo with your VM system and CMDB data.

Contact us for a demo

Customers