

 Piergiorgio Venuti
Introducing a set of new GDPR tools
GDPR tools
GDPR, the European Union regulation aimed at strengthening and unifying data protection for all individuals within the European Union comes into force on 25th May. The regulation brings a huge change to European data security, but it also impacts many non-EU based business as well. If you’d like to find out more about GDPR you can read our previous blog post.
We have introduced numerous changes within our portal to ensure that data protection complies with the GDPR
GDPR tools
Get consent with GDPR-friendly forms
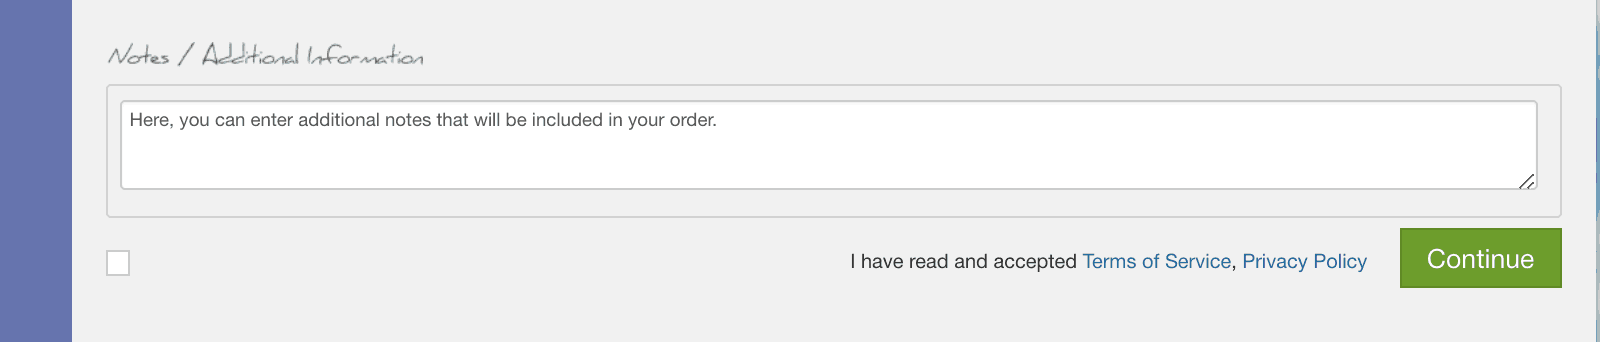
The GDPR sets a high standard for consent for gathering and processing personal data. Consent requires a positive opt-in, which means you can’t use pre-ticked boxes or any other method of default consent. Explicit consent requires a very clear and specific statement of consent and the consent requests must be separate from other terms and conditions.
In addition to what we did for the order we add explicit check box in our registration form as well.
Highest professional standards of data handling.
Cyberfero now offers a set of features that are aimed at providing your customers with the best standards for data processing.
♦ Data retention
◊ Automatically remove empty client profiles after 6 months since sign-up. [bg_collapse view=”button-blue” color=”#ffffff” expand_text=”Show More” collapse_text=”Show Less” ]Client profiles that does not have any of the following:
1) Paid invoices
2) Active hosting account
3) Registration domain
4) Unclosed support ticket[/bg_collapse]
◊ Automatically remove inactive client profiles after 120 months since last payment. [bg_collapse view=”button-blue” color=”#ffffff” expand_text=”Show More” collapse_text=”Show Less” ]Client profile the does have paid invoices on file, but does not have any active account/domain or unclosed support tickets.[/bg_collapse]
♦ Deletion Handling: When client request deletion his account status will be changed to Pending removal, it will be removed after Deletion delay period.
♦ Deletion Delay: Permanently remove client data after 30 days (since last login)
♦ Export / report settings:
◊ Contacts
◊ Accounts / Services
◊ Domains
◊ Change log
◊ Transactions
◊ Invoices
◊ Tickets
The right to be informed
Under GDPR individuals have the right to be given information about how their data is being processed and why. We created multiple policy links (for separate terms) that client needs to accept in client portal, by ticking the relevant checkbox. Agreeing on the given terms will be required for the customer to proceed to checkout.
The right to access
Individuals have the right to obtain the confirmation as to whether or not personal data concerning them is being processed, where and for what purpose. In the client portal each registered client has access to the overview of their personal information. Under My Account→ Overview client can view their details along with the purpose for each data that is being collected (billing or non-billing; defines whether or not the data is needed for invoicing and hence it may be required to keep that data for a given period of time).
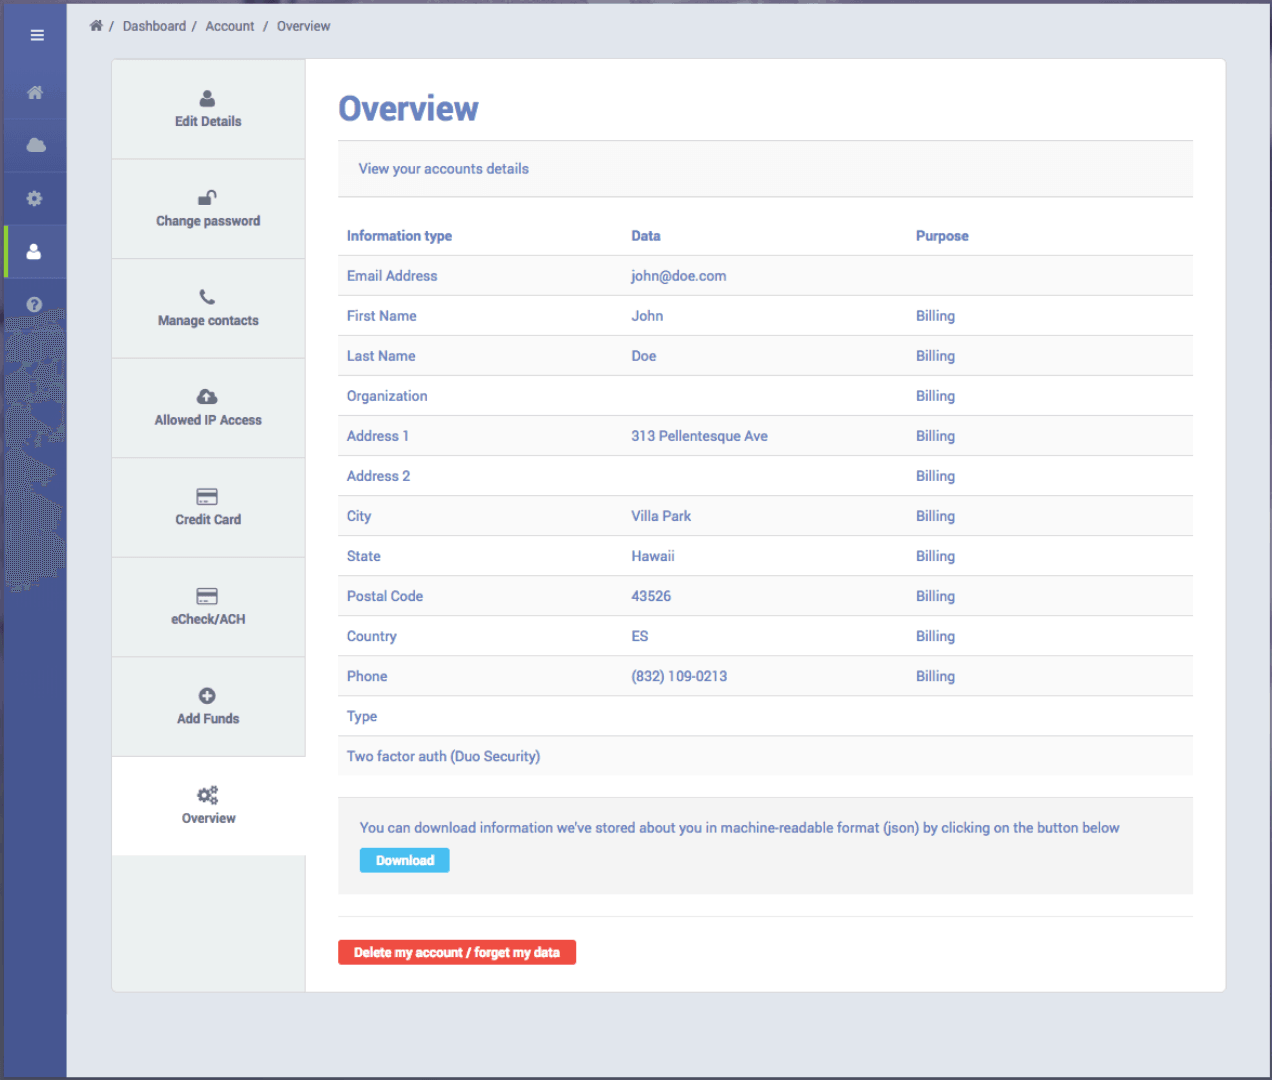
Cyberfero admin area also provides you with the possibility to generate PDF report with client data, the json file contains other information (such as c
The right to be forgotten
GDPR gives individuals the right to have their personal data erased. With Cyberfero, clients can request to have their account deleted and their data forgotten with just one mouse click. We’ve made sure that the client will be able to start the account removal process only if there are no unpaid invoiced linked to their account and there are no active services that can’t be cancelled. Requesting the account to be deleted will assign the account with the ‘pending removal’ status and deleted after certain period of time (30 days).
If a client requests for their data to be forgotten but are required to keep their data for a given period of time (for legal or tax purposes etc). we have the possibility to remove as much client information as possible, without removing the data required for billing/contract purposes. Cyberfero’s client anonymization feature allows us to close client profile, terminate client services, clear client changes log, emails and tickets and remove ALL non-billing data.
The right to object
Individuals have to right to object at any time to processing of personal data concerning them. With Cyberfero our clients can review all of the terms and services they have given their consent to and withdraw that consent at any time. All changes made to client profile are logged, so if needed we can prove that the customer has given us the consent to gather/process their data (and when) and if the customer withdraws the consent we can determine when it happened.
Cyberfero Newsletter module for email and e-commerce marketing also provides quick and easy ‘unsubscribe’ option in each email send to the customer.
The right to data portability
As per GDPR individuals have the right to receive a copy of the personal data, free of charge, in an electronic format. Cyberfero enables to easily downloaded to the json file all personal information gathered in client profile with the single click of the mouse from My Account→ Overview section in client area.
[btnsx id=”2931″]
Useful links:
Share


RSS
More Articles…
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company
- NIS: what it is and how it protects cybersecurity
- Advanced persistent threats (APTs): what they are and how to defend yourself
- Penetration Testing and MFA: A Dual Strategy to Maximize Security
- Penetration Testing: Where to Strike to Protect Your IT Network
- Ransomware: a plague that brings companies and institutions to their knees. Should you pay the ransom? Here is the answer.
- Why IT audit and log management are important for Cybersecurity
- Red Team, Blue Team and Purple Team: what are the differences?
Categories …
- Backup as a Service (18)
- Acronis Cloud Backup (11)
- Veeam Cloud Connect (4)
- Cloud Conference (3)
- Cloud CRM (1)
- Cloud Server/VPS (22)
- Conferenza Cloud (4)
- Cyberfero (15)
- ICT Monitoring (5)
- Log Management (2)
- News (25)
- ownCloud (4)
- Privacy (7)
- Security (203)
- Cyber Threat Intelligence (CTI) (8)
- Deception (4)
- Ethical Phishing (11)
- Netwrix Auditor (2)
- Penetration Test (11)
- Posture Guard (3)
- SOCaaS (65)
- Vulnerabilities (84)
- Web Hosting (15)
Tags
 Unknown Feed
Full Disclosure
- APPLE-SA-09-28-2026-3 macOS Sequoia 15.8.1 September 29, 2026Posted by Apple Product Security via Fulldisclosure on Sep 28APPLE-SA-09-28-2026-3 macOS Sequoia 15.8.1 macOS Sequoia 15.8.1 addresses the following issues. Information about the security content is also available at https://support.apple.com/149229. Apple maintains a Security Releases page at https://support.apple.com/100100 which lists recent software updates with security advisories. CoreGraphics Available for: macOS Sequoia Impact: Processing a maliciously […]
- APPLE-SA-09-28-2026-2 macOS Tahoe 26.7.1 September 29, 2026Posted by Apple Product Security via Fulldisclosure on Sep 28APPLE-SA-09-28-2026-2 macOS Tahoe 26.7.1 macOS Tahoe 26.7.1 addresses the following issues. Information about the security content is also available at https://support.apple.com/149228. Apple maintains a Security Releases page at https://support.apple.com/100100 which lists recent software updates with security advisories. CoreGraphics Available for: macOS Tahoe Impact: Processing a maliciously […]
- APPLE-SA-09-28-2026-1 iOS 26.7.1 and iPadOS 26.7.1 September 29, 2026Posted by Apple Product Security via Fulldisclosure on Sep 28APPLE-SA-09-28-2026-1 iOS 26.7.1 and iPadOS 26.7.1 iOS 26.7.1 and iPadOS 26.7.1 addresses the following issues. Information about the security content is also available at https://support.apple.com/149226. Apple maintains a Security Releases page at https://support.apple.com/100100 which lists recent software updates with security advisories. CoreGraphics Available for: iPhone 11 […]
- SEC Consult SA-20260923-0 :: Local Privilege Escalation in Honeywell IQ MultiAccess Update Service #CVE-2026-13742 September 27, 2026Posted by SEC Consult Vulnerability Lab via Fulldisclosure on Sep 26SEC Consult Vulnerability Lab Security Advisory < 20260923-0 > ======================================================================= title: Local Privilege Escalation product: Honeywell IQ MultiAccess Update Service vulnerable version: IQ V27 & IQ V28 fixed version: IQ V27 SP1 & IQ V28 SP1 CVE number: CVE-2026-13742 […]
- [SYSS-2026-071]: GDCM (Grassroots DICOM) - Format String (CWE-134) September 27, 2026Posted by Matthias Deeg via Fulldisclosure on Sep 26Advisory ID: SYSS-2026-071 Product: GDCM (Grassroots DICOM) Manufacturer: GDCM Project Affected Version(s): 3.3.0 Tested Version(s): 3.3.0 Vulnerability Type: Format String (CWE-134) Risk Level: Medium Solution Status: Open Manufacturer Notification: 2026-07-24 Public Disclosure: 2026-09-23 CVE Reference: Not yet assigned Author of...
- [SYSS-2026-070]: GDCM (Grassroots DICOM) - Integer Overflow (CWE-190) September 27, 2026Posted by Matthias Deeg via Fulldisclosure on Sep 26Advisory ID: SYSS-2026-070 Product: GDCM (Grassroots DICOM) Manufacturer: GDCM Project Affected Version(s): 3.3.0 Tested Version(s): 3.3.0 Vulnerability Type: Integer Overflow (CWE-190) Risk Level: High Solution Status: Open Manufacturer Notification: 2026-07-24 Public Disclosure: 2026-09-23 CVE Reference: Not yet assigned Author of...
- [SYSS-2026-069]: GDCM (Grassroots DICOM) - Integer Overflow (CWE-190) September 27, 2026Posted by Matthias Deeg via Fulldisclosure on Sep 26Advisory ID: SYSS-2026-069 Product: GDCM (Grassroots DICOM) Manufacturer: GDCM Project Affected Version(s): 3.3.0 Tested Version(s): 3.3.0 Vulnerability Type: Integer Overflow (CWE-190) Risk Level: High Solution Status: Open Manufacturer Notification: 2026-07-24 Public Disclosure: 2026-09-23 CVE Reference: Not yet assigned Author of...
- [SYSS-2026-068]: GDCM (Grassroots DICOM) - Stack-based Buffer Overflow (CWE-121) September 27, 2026Posted by Matthias Deeg via Fulldisclosure on Sep 26Advisory ID: SYSS-2026-068 Product: GDCM (Grassroots DICOM) Manufacturer: GDCM Project Affected Version(s): 3.3.0 Tested Version(s): 3.3.0 Vulnerability Type: Stack-based Buffer Overflow (CWE-121) Risk Level: High Solution Status: Open Manufacturer Notification: 2026-07-24 Public Disclosure: 2026-09-23 CVE Reference: Not yet assigned...
- [SYSS-2026-067]: GDCM (Grassroots DICOM) - Stack-based Buffer Overflow (CWE-121) September 27, 2026Posted by Matthias Deeg via Fulldisclosure on Sep 26Advisory ID: SYSS-2026-067 Product: GDCM (Grassroots DICOM) Manufacturer: GDCM Project Affected Version(s): 3.3.0 Tested Version(s): 3.3.0 Vulnerability Type: Stack-based Buffer Overflow (CWE-121) Risk Level: High Solution Status: Open Manufacturer Notification: 2026-07-24 Public Disclosure: 2026-09-23 CVE Reference: Not yet assigned...
- harness Gitspace hardcoded password for every user account September 27, 2026Posted by Khashayar Fereidani on Sep 26# harness Gitspace hardcoded password for every user account **Author:** Khashayar Fereidani **Disclosure Date:** 2026-09-24 **Advisory:** https://fereidani.com/harness-gitspace-hardcoded-password-for-every-user-account **Contact:** https://fereidani.com/contact ## Description Gitspaces are Harness's hosted development environments: a container with the user's source tree, running an SSH server and an IDE, with its ports published on...
Customers


Twitter FEED
Recent activity
-
SecureOnlineDesktop
Estimated reading time: 6 minutes L'impatto crescente delle minacce informatiche, su sistemi operativi privati op… https://t.co/FimxTS4o9G
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The growing impact of cyber threats, on private or corporate operating systems… https://t.co/y6G6RYA9n1
-
SecureOnlineDesktop
Tempo di lettura stimato: 6 minuti Today we are talking about the CTI update of our services. Data security is… https://t.co/YAZkn7iFqa
-
SecureOnlineDesktop
Estimated reading time: 6 minutes Il tema della sicurezza delle informazioni è di grande attualità in questo peri… https://t.co/tfve5Kzr09
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The issue of information security is very topical in this historical period ch… https://t.co/TP8gvdRcrF
Newsletter
Products and Solutions
Partners
Cloud Models
News
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company May 6, 2024
- NIS: what it is and how it protects cybersecurity April 22, 2024
- Advanced persistent threats (APTs): what they are and how to defend yourself April 17, 2024
- Penetration Testing and MFA: A Dual Strategy to Maximize Security April 15, 2024
- Penetration Testing: Where to Strike to Protect Your IT Network March 25, 2024
Google Reviews
Davvero consigliata !!!!!
In particolare vorrei sottolineare la figura che piu’ racchiude e sintetizza le qualità della Secure Online Desktop , il suo AD Ing. Piergiorgio Venuti, professionista impagabile , sia dal punto di vista tecnico/organizzativo che soprattutto (e non dimeno) come persona , capace di gestire , risolvere e approcciare qualsivoglia attività/problematica, davvero un grande !!!!



Tempi veloci e staff preparato!
Ottima azienda, servizi molto utili, staff qualificato e competente. Raccomandata!read more
Ottimo supportoread more
E' un piacere poter collaborare con realtà di questo tiporead more
Un ottimo fornitore.
Io personalmente ho parlato con l' Ing. Venuti, valore aggiunto indubbiamente.read more

About
© 2024 Cyberfero s.r.l. All Rights Reserved. Sede Legale: via Statuto 3 - 42121 Reggio Emilia (RE) – PEC [email protected] Cod. fiscale e P.IVA 03058120357 – R.E.A. 356650 Informativa Privacy - Certificazioni ISO