

Estimated reading time: 6 minutes
Today we see one of the latest additions to our SOCaaS, the Autonomous Threat Sweeper (ATS) . A system able to support SOC in an innovative way and protect against the most innovative threats.
The Privacy Guarantor, through the provision dated May 27, 2021, has introduced some changes regarding the violation of sensitive and personal data. A particular reference was made to the numerous cases of data breach. In essence, the legislation relating to the notification system has been tightened . The legislation provides for the application of a certain procedure to be adopted in the event of a data breach.
It is not easy to stay up to date on the continuous regulations on privacy, nor to have IT threat prevention systems available such as i ransomware working in the shadows and increasingly aggressive and dangerous. For this reason, threat protection has become an issue that is no longer easily manageable through non-professional systems . Today specific IT skills are constantly updated and professionals working in the sector, especially for companies.
Context: the unstoppable growth of ransomware
As we know, the term ransomware defines a category of malware capable of encrypting the files and documents contained in the attacked computer, in some cases even on the network to which it is connected. We have seen this in various articles through known examples .
In recent years, ransomware has spread enormously, so much so that it is listed as the most dangerous cyber threat to businesses .
Among the main companies targeted are those that have a large amount of sensitive data which, if stolen, would expose the company to the distrust of their customers. The encryption of the files stored inside the devices is, therefore, resolved only following the payment of a ransom.
Unfortunately, once compromised, the system does not allow users to access the data on their devices, effectively preventing their use.
Currently, ransomware is one of the main cyber threats, so much so that it is categorized as a profitable business model. This is because of the constant improvements made to their software that make it easier for hackers to use. The result is an increasing number of attacks performed with tools that required almost no specific skills.
IT security: increased risk = increased insurance policies
In terms of computer security, the aspects to consider are different, among these, in fact, there is the one related to ransomware software. These require a greater definition of reporting requirements in the event of a data breach due to an increase in systemic risk.
This problem has led to an increase in the prices of the insurance market. As these threats, in addition to being more and more frequent, are the cause of high damage to companies, insurance companies have raised their prices. But not only that, today they also demand specific requirements from the policyholders, to demonstrate the use of adequate defense systems in the IT field.
Autonomous Threat Sweeper: the new technology integrated in SOCaaS
Preventive malware detection is the priority solution to be adopted in order to avoid the risk of being attacked by malware that can steal company data.
What is worrying, however, is not only the increase in the cost of insurance, but the greater definition of the required requirements. The requirements, that is, relating to the reports to be forwarded in the event of a data breach and the consequent increase in systemic risk .
The SOC as a Service is a service entirely dedicated to the IT security of companies, which involves data collection and enrichment aimed at proactive identification of social engineering attacks. The system includes a Security Data Lake (SDL), the event and information management (SIEM) and l ‘user behavior analysis (UEBA).
Through the Autonomous Threat Sweeper (ATS) the team is able to provide companies with 24/7 coverage through an automatic search. This, once activated, is able not only to to prevent attacks from the outside, but also to detect any malware previously installed on company devices.
This system allows you to automate the rapid detection of these threats. Once identified, it is easy to implement targeted actions in order to counter their attacks. Since cyber attacks are and will always be present in everyday business life, it is certainly important to be well equipped. Attacks will continue to grow in breadth and scale and let’s not forget the trend in the shortage of technicians . We can only bring into play systems that automate the first stages of control and detection.
The Autonomous Threat Sweeper (ATS) is currently one of the few systems capable of pre-coding the latest generation of cyber attacks . Its coverage includes corporate networks and devices.
Autonomous Threat Sweeper (ATS)
Autonomous Threat Sweeper (ATS) is a constantly updated system capable of detecting the latest generation threats. This guarantees companies that turn to us to always be protected from the latest generation IT risks to infrastructures and devices.
We have already talked about SIEM , software tools able to provide cyber security professionals with an analysis of logs and events to provide real-time threat minitoring. Here, the ATS even improves the functionality of software as complex and accurate as SIEM, making it capable of detecting low and slow threats through post-hoc.
Basically, with the ATS it will be possible to speed up the process of detecting threats in order to avoid damage that also compromises the strength of the infrastructure.
Conclusions: How to behave in case of violation
In the event that an IT breach occurs, with or without intent, involving the loss, destruction, modification or unauthorized disclosure or unauthorized access to the data processed by a company, the data controller appointed by the same must notify the violation within 72 hours.
Subsequently, investigations could take place to understand the extent of the damage and then also penalties in case of negligence. By adopting an Autonomous Threat Sweeper your business will be able to intercept threats before they can do any harm.
Preventing data breaches, ransom requests and other cyber security attacks is easy if you turn to competent people. Ask us for more details on how we can support your company with regards to cybersecurity. We will be happy to answer all your questions.
Useful links:
Webinar: SOCaaS (Security Operation Center as a Service) e NGS (Next Generation SIEM)
Pass the Ticket: how to mitigate it with a SOCaaS
Use cases of a SOCaaS for companies part 2
Use cases of a SOCaaS for companies part 1
Predictive cybersecurity with our SOCaaS
Cyberattacks are numerous and do not distinguish between companies and individuals when targeting a target. You’ve most likely heard the term “cyber threat” in the media before, but what exactly are we talking about? Other ways you may have heard this are “cyberthreat”, “cyberattack” or similar.
What is a Cyber Threat?
Today the term “cyber threat” is used predominantly in the world of information security.
A cyber threat is a malicious act conceived with the purpose of damaging systems, stealing data or any purpose that has the purpose of causing damage of any kind. Viruses, data breaches and DDoS attacks are included. Even if the threat is virtual, what is real is the attacker’s intent as well as the potential impact. While many cyberattacks are mere nuisances, some are quite serious. Some even potentially threaten human lives.
The potential impact that these kinds of attacks can have is often underestimated. Most of the time, the attacks are easily identifiable and do not pose much risk. Instead, other times it happens to come across some more sophisticated threats, difficult to identify, which represent a big problem even for many companies.
Cyber threats are a major concern for businesses. Cyberattacks can lead to power outages, government equipment failures, and breaches of state secrets. They can manipulate telephone and computer networks or, as in the case of ransomware, they can cripple entire systems by making data inaccessible.
Every day new companies and organizations set foot in the digital world with awareness of the risks associated with their technological infrastructures. In some cases, cyber threats are underestimated and this often means great economic and image damage for the company that has underestimated cyber threats and security.
The increase in IT-related risks is real, as are data security solutions. The best thing to do is to take the necessary safety measures right away.
Types of Cyber Threats
The types of cyber threats are numerous, and it must also be considered that they are constantly evolving. The intent of hackers is usually to secure an economic gain by carrying out sabotage, espionage or data theft operations. As a result, they can be expected to do everything possible to achieve their ends.
Virtually every cyber threat falls into one of the following ten types of risks. Hackers have an abundance of options to choose from in order to operate. Furthermore, computer literacy is all in all poor, so hackers often have an easy time, especially for small local realities.
The 10 most common types of computer threats
Malware
It is a type of software that executes a malicious command on a device or within a computer network, corrupting data or taking control of the system.
Phishing
Phishing is an e-mail attack that consists of tricking the recipient into revealing confidential information or inviting him to download malware by clicking on a link in the body of the message. These are real scams, which we have talked about extensively in other articles. Often they don’t even involve great IT skills on the part of the attacker, just a little social engineering.
Vishing
Vishing is a more sophisticated form of phishing in which the hacker uses VoIP technology to contact the victim, attempting to trick them. There is also a variant that instead uses text messages to attack, it is called smishing.
Man in the Middle
As the name suggests, this type of attack refers to when a hacker intervenes in a conversation posing as one of the two parties, with the aim of stealing sensitive information. What we often don’t think about is that the conversation is between two machines and therefore not immediate to monitor.
Trojan viruses
The origin of its name is inspired by the famous Trojan Horse of ancient Greece. Trojan is a type of malware that infiltrates a computer system by hiding its true nature. For example, it could impersonate known software and then release malicious code once inside the host device.
Ransomware
Ransomware is an attack that uses encryption to make information on a system inaccessible. The aim is to demand a ransom in exchange for being able to access the data again. Possibilità che a volte, in realtà, non è nemmeno assicurata.
DDoS attack
It occurs when the attacker uses many devices to overload a target, such as a website, with requests, causing it to crash or become instabilities.
Attacks on IoT devices
This is an increasingly popular attack due to the nature of the targets. Devices such as sensors or industrial plants connected to the network are vulnerable to multiple types of cyber threats. The hacker could take control of the device and then later use it in a DDoS attack. Alternatively it could steal the information present in the device itself obtaining important data to continue the attack. Given their number of frequently out-of-date operating systems, IoT devices are a very attractive target.
Malware in mobile applications
Phones and tablets are just as vulnerable to malware as any other device. È possibile inserire malware all’interno di app, nei siti web o nelle e-mail sfruttando il phishing. Once compromised, a mobile device can provide access to personal information, location data, and financial accounts.
A recent example of this type of eventuality is Pegasus software, which is used to monitor and collect data from journalists around the world. (Source: The Guardian)
Practical defense and prevention solutions
Cyber threats are always expanding and improving. Millions of them are created every year, many of them follow the aforementioned characteristics, but others are technologically more complex and more powerful.
Fortunately, however, there are also more and more highly qualified companies in the field of IT security that offer cutting-edge tools and services that help prevent, identify and promptly block all kinds of IT attacks.
Threat detection tools
Threat detection tools are an essential part of a company’s cybersecurity technology stack. Threat detection is also the first defense against any Cyber Threat.
Specific solutions, such as the use of a SOCaaS, for example, are of vital importance for safeguarding an IT infrastructure, thanks also to the integration of the SIEM engine which includes UBA and UEBA, guaranteeing complete control also over the users.
Another useful tool is definitely ACP. Acronis Cyber Protect is a solution that integrates data protection and management to safeguard your endpoints, data and systems. Its automation capabilities provide unparalleled protection, enabling businesses to increase their productivity and reduce risk.
Vulnerability Assessment & Penetration Test (VA-PT)
Services like VA & PT are field tests that test the infrastructure in a concrete context. Our teams of white hat hackers find vulnerabilities within the system to point the finger at weaknesses to fix.
Conclusions
We have learned what a cyber threat is and its most common types, also discovering which solutions can be adopted in order to guarantee better corporate and employee safety.
What countermeasures has your company taken to protect your safety? If you would like more information about it, you can contact us by pressing the button below. We offer ad hoc services and solutions to strengthen corporate defenses.
Useful links
Estimated reading time: 6 minutes
Is the threat of a large-scale DDoS attack enough to convince organizations to bow to a ransomware attack?
It might be a good time for companies to invest in DDoS protection , as hackers have begun to use the threat of large-scale DDoS attacks to carry out ransomware attacks on organizations .
According to a new blog post from Cloudflare, a major company, in the Fortune Global 500, was the target of a DDoS ransomware attack ( RDDoS ) in late 2020. The attacking group claimed to be Lazarus Group , North Korea’s largest and most active hacking division .
This extortion attempt was part of a larger trend of ransom campaigns that has been developing throughout the past year . Cybercriminals will likely continue to use similar methods, as they have been quite successful.

What is a DDoS Ransomware?
Unlike a ransomware attack in which cybercriminals enter a company’s network in order to block their files, RDDoS attacks use the threat to obscure the Dell website. ‘company with traffic overload and this can be crippling for business.
Just as an organization can use cloud backup and other similar services to protect its data from being blocked following a ransomware attack, DDoS protection ensures that a company’s website remains secure if it is suddenly flooded with traffic overload.
What is a DDoS attack?
Before continuing and to better understand what we are talking about.
DDoS is an acronics which means Distributed Denial of Service . Attacks of this type target websites and online services. The goal is to flood the site with more traffic than the server or network can accommodate . The purpose is to make the website or service unusable.
Traffic can consist of inbound messages, connection requests or fake packets. In some cases, victims are threatened with a DDoS attack or attacked at a low level . This attack can be combined with an extortion threat than a more devastating attack unless the company pays a ransom in cryptocurrency . In 2015 and 2016, a criminal group called the Armada Collective repeatedly extorted money from banks, web host providers and other companies using this method.
How Do DDoS Attacks Work?
The theory behind a DDoS attack is simple: flood a server with requests so that it reaches the limit that available resources allow. If the attack is successful, your server, service, website or network is rendered inoperable.
The primary way a DDoS is accomplished is through a network of remotely controlled, hacked or bot computers . These are often called “zombie computers”, we have also seen them in the techniques of Zombie Phishing . These zombies , organized in networks called botnets , are used to flood websites, servers and networks with more data than they can accommodate.
Botnets can send more connection requests than a server can handle or send huge amounts of data that exceed the bandwidth capabilities of the targeted victim. Botnets can range from thousands to millions of computers controlled by cybercriminals. Your computer could be part of a botnet without you knowing.
What are the symptoms of an attack?
DDoS attacks have distinctive symptoms . The problem is that the symptoms are so similar to other problems you may have with your computer that it can be difficult to understand without a professional diagnosis. Symptoms of a DDoS include:
- – Slow file access, both locally and remotely
- – Inability to access a particular website
- – Logout from the Internet
- – Problems accessing all websites
- – Excessive amount of email spam
Most of these symptoms can be difficult to label as unusual . However, if two or more occur over long periods of time, you could be the victim of a DDoS and check them out.
Phenomenology of a DDoS Ransomware Attack
A DDoS ransomware attack is like pointing a gun at someone and asking them for their wallet. It is not known if the gun is real (or loaded), but to avoid an unpleasant misunderstanding, the money is handed over.
In these attacks, in fact, the hackers threaten to carry out the attack, but have not yet performed any. In some cases they launch a minor attack as a demonstration action.
The attack covered in the Cloudflare article started like many other attacks, with ransom emails sent to employees of the organization. These emails contained a note that read:
Please do a Google search of “Lazarus Group” to take a look at some of our previous work. Also, search for “NZX” or “New Zealand Stock Exchange” in the news. You don’t want to be like them, do you?
The current price is 20 Bitcoin (BTC). It’s a small price to pay for what will happen if your entire network goes down. Is it worth it? You decide!…
If you decide not to pay, we will start the attack on the indicated date and will keep it until you do. We will completely destroy your reputation and make sure that your services remain offline until you pay… “.
The attackers then began sending a large amount of traffic to one of the company’s global data centers , firing gigabits of data per second to a single server. This led to a DDoS event and generated a series of unpleasant inconveniences.
Next, the criminals launched an attack at the end of a working day that was difficult to mitigate due to the fact that the organization was still using services to mitigate previous attacks.
Mitigating DDoS attacks can be quite difficult when an attack is already underway, which is why companies should consider using dedicated and proactive DDoS protection .
We will likely see an increase in similar attacks this year , so now is the time to take the necessary precautions or risk having the company’s website taken down or worse, having to pay a ransom in order to continue with the services offered.
The Cyberfero proposal for companies
Due to the possibility that these DDoS Ransomware attacks become more and more frequent, we think we are a good time to evaluate one of our services in this regard.
CDN against DDoS ransomware attacks
One way to mitigate attacks is by using CDN ( Content Delivery Network ) services such as Cloudflare . These services distribute a static copy of the site on their servers around the world. When the site is requested by a client, the request is processed by the closest CDN server, reducing the loading time.
The use of this type of service filters access to the company site by distributing traffic to other servers that keep a copy of the site.
In this way, not only is the site loaded via the CDN server closest to the user, reducing the loading time, but the traffic is distributed territorially and what actually reaches the server is a fraction of the real one .
For customers of the Cyberfero Webhosting service, the Cloudflare CDN network is made available for free .
For our customers who use different services, it is necessary to design an ad-hoc solution. Contact us to find out more.
Useful links:
Useful links:
Protecting a site in WordPress: security package
Server hosting for Cyberfero website
Estimated reading time: 4 minutes
ransomware gangs have been targeting businesses in recent times, demanding larger payments than they can extort from consumers. The plan was very successful. According to the new data, 70% of the attacked companies paid the ransom to get their data back. Avoiding ransomware is a necessity, these figures implicitly prove it. If such a large number of companies pay, it is because the risk is too great in terms of reputation and collateral economic losses.
Researchers from IBM Security’s X-Force interviewed executives of 600 companies of all sizes and found that organizations affected by ransomware choose to pay in most cases.
Data shows that 20% of compromised organizations paid ransoms of more than $ 40,000 and 25% paid between $ 20,000 and $ 40,000. These numbers are much higher than that. that consumers typically pay, which is usually around $ 500-1,000, depending on the variant of the ransomware.
When targeting businesses, hacking groups aim to paralyze organizations by encrypting financial data , customer databases, sales data and other vital information .
Avoid ransomware – the risks of attacks
In the past year, a number of organizations have been hit by severe ransomware attacks, including hospitals, universities and others. For example, the San Francisco Municipal Transportation Authority was hit by a ransomware attack during the weekend of Thanksgiving, a very important holiday in the US. The attack paralyzed desktops within the agency and forcing officials to shut down the automatic ticket machines. Needless to say, this attack resulted in a huge loss of assets and a ransom demand.
Getting malware into public organizations isn’t as difficult as you might think, and is often done with a single email .
In their attacks on networks, cybercriminals seek out the servers that keep the business running and encrypt critical assets rather than working on enterprise-wide endpoints.
The access point is usually a phishing email with a malicious attachment, sent to the mailbox of a employee . In most cases, the attachment is a Microsoft Office document asking the victim to enable macros . Clicking the macro enable button is often a trivial matter for those uninformed users who just want to get rid of the warning at the top of the document . The malware runs as soon as the user allows the macros to run. The ransomware can also arrive through any other attachment or through exploit kits which facilitate infection without any special action on your part.
Economic losses
The amount of money businesses have paid to get their data back shouldn’t come as a surprise considering the alternative. As is increasingly the case, the attack doesn’t just put key the data until payment of the requested amount. The threat continues with the release of data if you do not agree to pay a second ransom. In the end two ransoms will be paid and in any case there is no certainty that the data will not be disclosed. (It is said double extortion attack).
Many organizations keep these attacks under wraps to avoid public humiliation and loss of customer confidence . Data from the IBM survey shows that 29% of executives in large corporations would pay more than $ 50,000 to retrieve financial data.
Law enforcement, including the FBI, and security experts advise ransomware victims not to pay, for a variety of reasons. First, there is no guarantee for the attacker to deliver the decryption key. Second, the ransomware’s profits help fund other cybercrime operations.
How to defend yourself to avoid ransomware
Phishing remains one of the key methods by which a ransomware attack is attempted. With the recent increase in remote working, it is imperative to reiterate the importance of being careful when opening emails and attachments . If employees are suspicious of something, they should report it.
Organizations should also make sure they have a good patching strategy and apply the latest security updates . This prevents cybercriminals from taking advantage of known vulnerabilities to distribute malware.
Regularly updating backups should be a priority , because if the worst happens and your organization falls victim to a ransomware attack, your network can be restored without paying the ransom.
Cyberfero provides solutions for the situations listed through the SOCaaS service. You can ensure the protection of a Security Operation Center without having to invest in its initial funding .
The system controls the actions of the computers connected to the network using an artificial intelligence. As soon as a suspicious, even legitimate, action is detected, the technicians are alerted who can investigate the nature of the fact . The new generation SIEM systems and behavioral analysis via UEBA , work together to offer 360 ° security.
Cyberfero also provides intelligent anti-ransomware backup systems via Acronis Cyber Protect Cloud . With this tool at your side, business and customer data are safe. Any attack attempt is identified and mitigated immediately, meanwhile, thanks to dynamic backups, the data is immediately restored .
Avoiding ransomware can be relatively easy – just pay attention to every operation you perform on your computers. Unfortunately, sometimes this is not enough. This is the time when having invested in a quality safety system will make a difference.
For questions or requests do not hesitate to contact us, we will be happy to answer your questions and propose a solution tailored to your needs.
Estimated reading time: 8 minutes
Looking to up the ante and earn more money with the ransomware , i Cybercriminals are increasingly using a tactic known as double extortion ransomware . Not only do they encrypt data and demand a ransom from the victim to regain access. They also threaten to upload them online if their conditions are not met.
Let’s take a step back, ransomware is one of the most common types of malware. It targets a company every 14 seconds and it cost $ 11.5 billion in 2019 alone . Typically, hackers who carry out these attacks break into a system to steal data and delete it if the victim doesn’t pay a ransom.
Why do hackers prefer double-extortion ransomware?
The rise of double extortion ransomware proves that cybercriminals are constantly expanding their arsenal. Paolo Passeri, director of cyber intelligence at the software firm Netskope , says these attacks they have become popular because they are the easiest way for hackers to make money.
Passeri Says: “With double extortion ransomware attacks, even if a backup is available, attackers can put more pressure on the victim to pay the ransom . The increased pressure comes from the potentially serious consequences of a data leak, for example economic and reputational damage. Groups like REvil are even more creative: they don’t just leak data, they monetize it by auctioning it on the dark web and putting even more pressure on their victims. “
When conducting a double extortion ransomware attack, hackers start spending more time on the overall strategy . Sparrows warns that scammers are no longer taking an opportunistic approach. Instead, they are carefully selecting their target and method of attack to increase the ransom money they make . He explains: “ the threat actors select their victims, choosing organizations whose businesses could be affected by a data leak “.
The spear phishing is the primary means of distributing double extortion ransomware, but cybercriminals are also by exploiting vulnerabilities in on-premises devices such as VPN concentrators. “In the past few months, nearly all major VPN technologies have suffered severe vulnerabilities that have been exploited for similar attacks,” says Passeri.
“This is unfortunate given the current situation with forced telework where these remote access technologies play a crucial role in ensuring business continuity during Covid-19. These systems are directly exposed to the Internet, so threat actors can scan them and then exploit any vulnerabilities discovered “.
Risks of Doxing : diffusion of private data
Double extortion ransomware provides more opportunities for cybercriminals, allowing them to extort victims twice. They can ask for a first payment to decrypt the files and a second payment not to make them public.
This technique, also known as doxing , is been used by an increasing number of ransomware groups over the past year. The consequences of doxing are more severe for the victim, so they often come down to demands. This means more money in the pockets of cybercriminals to fund new strains of ransomware and support other criminal activities.
Improvements in malware and financial incentives for hackers have led to the growth of double extortion ransomware attacks. In the past, ransomware encrypted files and hackers stole data, but it was rare to do both.
We now have bots that can scan the web for unprotected data, steal it, encrypt it or delete it, and leave a ransom note for the owner, all in one automated attack. The hacker can then collect a ransom for the data and sell the data to other criminals, playing double-crosses with minimal effort .
An aggressive-tactic
There has been an influx of double extortion ransomware attacks in the past year. Hackers gained traction in late 2019 when high-profile groups like Maze began exploiting aggressively this tactic.
In these particularly aggressive cases, the hacker would extract a copy of the data before encrypting it . This way the attacker not only prevents the victim from accessing her data, but also keeps a copy of the data for himself.
To claim responsibility and put pressure on the victim during the negotiation process, the attacker often released small chunks of data online. If the deals are blocked or failed, the attacker publishes all the stolen data or sells it to third parties . This creates a significant violation against the victim.
What to do
To defend against these attacks, there are several steps companies should take . For example, keeping systems updated to ensure that known vulnerabilities are resolved. It is also imperative that organizations have a layered security approach that includes the use of data loss prevention tools . An example is the service offered by Cyberfero Acronis Cyber Protect Cloud . The system can stop the extraction or encryption of the data which initiates these double extortion attacks.
But what can organizations do if they can’t successfully mitigate one of these attacks?
Organizations should try to include a last line of defense that isolates and stops illegitimate encryption immediately . This mitigates the risk when traditional prevention-based security has been compromised or bypassed. Robust backup processes, including air-gap backups, should also be considered to make it more difficult for criminals to encrypt or disable critical data stores.
Consequences
If an organization falls victim to a double extortion ransomware attack, there are often dire consequences. Criminal groups are increasingly blatant, even dystopian names like Maze, Netwalker and REvil, are an indication of this inclination. Their pride leads them to display exfiltrated data as online trophies and even sponsor clandestine hacking contests to display their malware. In a kind of cyber show-off . < / p>
For the victims, the consequences can be devastating. Travelex, a currency exchange service, went into receivership with the loss of 1,300 jobs in the UK following a ransomware attack . During the heist, the cyber gang REvil asked the company to pay $ 6 million in 48 hours. The company has faced the threat of publishing credit card information, national insurance numbers and birth dates of its customers.
It is clearly critical that companies do everything they can to identify and stop these attacks before they cause more damage. Preventing these attacks proactively is much better than mitigating their effects, with all the financial costs and reputational damage they entail .
Most attackers gain access through human error . For this, together with technical measures such as internal data access management and back-up, staff training and supervision are key elements in an organization’s defenses .
Victims essentially have two choices, both of which are costly: if they refuse to pay, they face a catastrophic data breach with exposure to painful regulatory fines and civil demands; if they pay the ransom, they still have no guarantee that the data will be returned.
Handle double-extortion ransomware
While getting hit by ransomware can deal a severe blow to any business, companies should be cautious when asked to pay a ransom. Doing so could involve even greater risks . There is no certainty that these hackers will not ask for more money without releasing the data anyway.
It is important for companies to secure their networks and conduct mock test < / a> to mitigate the ransomware threat . Such simulated attacks will help spot vulnerabilities within the organization without the risk of facing serious financial problems and having to answer very difficult questions from customers.
Implementing strong resilience measures is the best way to prevent double extortion ransomware. Ransomware is often a secondary infection. Threat actors seek to exploit known vulnerabilities, particularly in relation to remote access protocols and applications that are critical for working from home.
Critical to mitigating this is ensuring that vulnerabilities are patched in a timely manner and that network data logs are monitored for any unusual activity or data exfiltration. < / strong> There is therefore a potential window of opportunity to remedy any primary infection (which precedes the ransomware) and thus prevent the ransom note process from developing.
Education
Organizations need to educate staff about the risks of double extortion ransomware and how it is executed . Individual users can also be of great help by being aware of the potential of unsafe attachments. They should also be cautious about clicking any email links received in any communication , particularly with the recent resurgence of Emotet , a known malware.
There are two defense strategies for dealing with double extortion ransomware. First, robust backups, to make sure you don’t your hands tied if hackers gain control of your data. Then, encryption, to make sure that if an attacker threatens to expose your data, it’s protected too.
These approaches should then be incorporated into a broader strategy: careful monitoring of the network that could allow attackers to be cut off, and promoting employee IT education not to fall victim to phishing attacks which are often the main cause of a ransomware incident.
The threat of double extortion ransomware is undeniable, with cybercriminals carefully targeting and creating these attacks in an attempt to increase the size of ransom.
Organizations often feel they have no choice but to pay the ransom to avoid the leak of sensitive data. But it’s actually a Russian roulette game and the stolen information can still find its way online. Therefore the focus must be on prevention and risk mitigation .
WastedLocker is ransomware attack software that began targeting businesses and other organizations in May 2020. It is known for its high ransom demands reaching millions of dollars per victim. It is the product of a group of highly skilled cyber criminals who have been operating for over a decade: Evil Corp.
Who is behind WastedLocker Ransomware
The group behind WastedLocker goes by the name of Evil Corp and some of the individuals associated with it have a long history in the world of cybercrime. The group is best known for managing the Dridex malware and botnet since 2011, but has also been responsible for creating ransomware programs over the years.
Through various episodes of criminal attacks, the group has been developing malware targeting mainly US companies since 2011. For this reason they have been known to the police for some time. After a period of inactivity, the group reappeared in January 2020 and their activity resumed as usual, with victims appearing in the same regions as before.
WastedLocker is a completely new program from Evil Corp that began infecting organizations in May 2020. It does not share the code with BitPaymer (a previously used software) but shows other similarities in the ransom note and per-victim customization. Evil Corp’s lack of activity between March and May could be explained by the group that was working on developing this new cyber threat as well as other tools that make up its toolset.
How does it work
According to Symantec reports, the infection chain for WastedLocker starts with a JavaScript-based attack framework. The framework, called SocGholish, is distributed as a fake browser update from warnings displayed on legitimate but compromised websites. Hacked news websites are a common vector.
The SocGholish framework is distributed as a ZIP file. Once opened and executed, it initiates a chain of attacks that involves downloading and running PowerShell scripts and the Cobalt Strike backdoor. Evil Corp has used this same distribution technique in the past to distribute the Dridex Trojan, so it has been part of its arsenal for a long time.
Once hackers gain access to a computer, they begin distributing various tools to steal user credentials. In addition, they can also increase privileges and perform a lateral movement to other machines. The attackers’ goal is to identify and gain access to high-value systems such as servers. They then implement an ad hoc binary file on the compromised machines for the victims.
The use of manual hacking and system administration tools are part of a trend observed in recent years. According to this trend, cybercriminals are increasingly adopting attack techniques that in the past were associated with cyber espionage. This trend poses a serious problem for smaller organizations that lack the budget and IT resources to deploy defenses against advanced threats, but are a frequent target for ransomware groups and other financially motivated cybercriminals.
WestedLocker in detail
WastedLocker uses a combination of AES and RSA encryption in its encryption routine which is similar to other ransomware programs. Each file is encrypted with a unique 256-bit AES key generated on-the-fly. These AES keys along with other information about the encrypted files are then encrypted with a 4096-bit public RSA key which is encoded in the WastedLocker binary. Attackers keep the private part of the RSA key pair needed to retrieve AES keys and decrypt individual files.
According to an analysis by Kaspersky Lab, the encryption routine is strong and correctly implemented. So the victims cannot recover their files without the attacker’s private RSA key. Because it is a manually distributed ransomware threat customized to each target, attackers generate unique RSA key pairs for each victim. I mean, the key received from one organization after paying the ransom will not work to decrypt the files of another affected organization.
Some distinctive aspects of WastedLocker
The WastedLocker ransomware has a mechanism that allows attackers to prioritize certain directories during the encryption routine. This is probably used to ensure that the most important and valuable files are encrypted first in case the encryption process is detected by the system administrators and stopped while it is in progress.
The malware appends an extension to files consisting of the victim’s name and the word “wasted”. Also, it generates a text file with the ransom note for each file, which means that each directory will contain hundreds or thousands of copies of the ransom note.
WastedLocker is designed to delete shadow copies (the default backups made by the Windows operating system) and tries to encrypt files on the network, including remote backups.
After the July 2020 attacks
The Securonix Threat Research Team (STR) is actively investigating the details of Wastedlocker ransomware critical attacks. These have reportedly already affected more than 31 companies, of which 8 are Fortune 500 companies.
Impact
Here are the key details regarding the impact of WastedLocker ransomware attacks:
– WastedLocker ransomware is relatively new, used by EvilCorp, which previously used the Dridex trojan to distribute BitPaymer ransomware in attacks against government organizations and businesses in the US and Europe.
– Evil Corp group is currently focusing on targeted attacks on multiple industry casualties in recent months. Garmin is one of the latest high profile victims attacked (officially confirmed by Garmin on July 27).
– The most recent ransom amount requested was $10 million and appears to be based on the victim’s financial data. Based on the available details, the ransom has probably been paid.
– To date, a mono-extortion scheme appears to have been used, ie with only encryption and no or minimal data loss.
How to defend yourself
Following the analysis of the attacks and the data available, we want to suggest methods of mitigation and prevention of attacks.
– Review the backup retention policies. Make sure these are stored in a location that cannot be accessed / encrypted by the operator who placed the targeted ransomware. For example, consider write-only remote backup.
– Implement a training program on the safety of end users (company employees). Since end users are the targets of ransomware, it is best that they are aware of the current risks. It is important that they are aware of the threat of ransomware and how it occurs.
– Patches of infrastructure operating systems, software and firmware. Consider the possibility of leveraging a centralized patch management system.
– Maintain regular, air-gaped backups of critical company / infrastructure data. An air-gaped backup and recovery strategy means making sure that at least one copy of your organization’s data is offline and not accessible from any network.
– Implement security monitoring, particularly for high-value targets, to detect in advance any malicious ransomware operator positioning activity.
As always, we at Cyberfero are available for advice and to suggest you which services you can implement for the safety of your company. Contact us to find out how we can help you keep your business defenses high.
Useful links:
There have been critical cases of ransomware of note lately. Tor Vergata University suffered an attack that knocked out about a hundred computers. Access to the systems by teachers and students has been blocked. The attack affected a number of documents related to COVID-19 research that were encrypted and then made inaccessible. In addition, two other noteworthy cases shook hospitals in September. The first took place in Germany, in Düsseldorf, where a woman lost her life following an attack that also blocked the machinery that kept her alive. The second happened in the USA and involved UHS (Universal Health Services). In that case, patient care was kept secure, but the IT applications were out of order.
For the uninitiated, ransomware-type attacks happen this way: attackers take possession of the data on a computer and remove or encrypt it. They ultimately render them unusable and require the victim to pay a ransom to free up the data again.
The costs of an attack
According to the Cost of a Data Breach report, a critical ransomware attack can cost an average of $ 4.44M. It is an impressive figure that should make us reflect on the value of data managed by companies and on their protection.
Let’s see in detail some attacks and what consequences they had.
A fatal ransomware
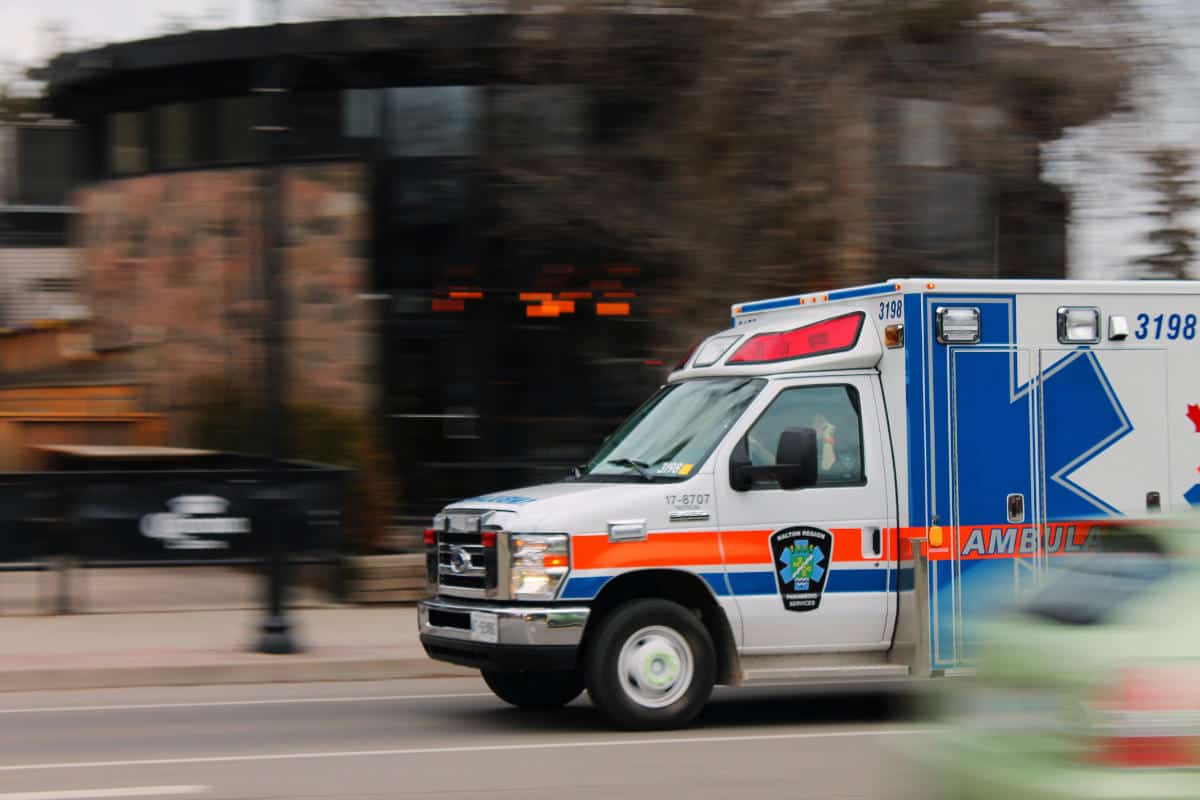
For the first time, a woman dies after a cyber attack on a hospital. On September 9, 2020, a critical ransomware attack, launched at a hospital in Düsseldorf, caused the vital systems to which the patient was connected to no longer function properly. The victim had to be transferred to another hospital as quickly as possible. For more than 30 kilometers, the paramedics fought for the victim’s life, but ultimately without success. Many questions remain pending regarding this case, first of all why the machines that kept the woman alive were connected to a hackable network. The investigations continue, however, showing how the network must be protected for the physical safety of users, to avoid tragic consequences.
An attack on research
The access of students and teachers was blocked at the University of Tor Vergata with a critical ransomware attack that made documents concerning the research on COVID-19 inaccessible. The attackers managed to break into systems within hours and encrypt files on hard drives. A month later, no ransom had yet been requested.
Such an attack could slow down the search, hampering the process. Even if no ransom was required, the damage would still be tangible.
Attack on UHS
Fortunately, it finished better than the attack in Düsseldorf, another episode hit areas close to health. Facilities using Universal Health Services (UHS) systems have seen access to the system freeze due to an attack. Fortunately, there were no casualties and patient care was guaranteed all the time, as stated by UHS itself.
Other critical ransomware attacks
Critical ransomware attacks happen all the time and can have non-immediate implications. For example, Fragomen, a New York law firm, suffered an attack and a consequent data breach involving the personal data of some Google employees.
Another attack hit Enel, which was asked for a ransom of € 14M in bitcoin. The attack refers to the download of private data, contacts, databases, financial and customer documents for a total of 4.5 TB. Enel did not provide any press release regarding the attack.
Run for cover
Unfortunately, ransomware attacks are among the most subtle and annoying, because they also leverage a psychological factor of the victim who sees a way out (payment) and tries to cover what happened in order not to lose reputation.Unfortunately, following a successful attack, the data is still breached and security has proved ineffective.
So how do you make sure these attacks are neutralized? Adequate security measures must be implemented to prevent attacks as much as possible and provide a quick response in critical situations.
Security services
Services such as those offered in partnership with Acronis and Cyberfero’s SOCaaS are essential tools for defending your data and corporate network. The first proposed service secures data through backups and monitors file changes. As soon as an encryption attempt is detected, the data is locked and secured to avoid the worst. In the unfortunate event that the attack is successful, backups reduce the severity of the consequences and prevent actual data loss.
SOC as a Service is an all-round solution that monitors all the IT infrastructure referred to. The defense is not specific to a type of attack, but instead focuses on detecting anomalies, even in user behavior, which can indicate ongoing attacks of all kinds.
Prevention
Finally, to verify that your system is protected, it is possible to request preventive services such as Vulnerability Assessment and Penetration Test. These test the infrastructures with controlled attacks in order to stimulate the security response and identify the areas that need to be reinforced. We recommend implementing this type of service regularly throughout the year as a preventative measure.
If you have any questions about the services or want to talk to us about your situation to request an intervention, do not hesitate to contact us, we will be happy to answer your questions.
Useful links:
Customers


Twitter FEED
Recent activity
-
SecureOnlineDesktop
Estimated reading time: 6 minutes L'impatto crescente delle minacce informatiche, su sistemi operativi privati op… https://t.co/FimxTS4o9G
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The growing impact of cyber threats, on private or corporate operating systems… https://t.co/y6G6RYA9n1
-
SecureOnlineDesktop
Tempo di lettura stimato: 6 minuti Today we are talking about the CTI update of our services. Data security is… https://t.co/YAZkn7iFqa
-
SecureOnlineDesktop
Estimated reading time: 6 minutes Il tema della sicurezza delle informazioni è di grande attualità in questo peri… https://t.co/tfve5Kzr09
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The issue of information security is very topical in this historical period ch… https://t.co/TP8gvdRcrF
Newsletter
Products and Solutions
Partners
Cloud Models
News
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company May 6, 2024
- NIS: what it is and how it protects cybersecurity April 22, 2024
- Advanced persistent threats (APTs): what they are and how to defend yourself April 17, 2024
- Penetration Testing and MFA: A Dual Strategy to Maximize Security April 15, 2024
- Penetration Testing: Where to Strike to Protect Your IT Network March 25, 2024
Google Reviews
Davvero consigliata !!!!!
In particolare vorrei sottolineare la figura che piu’ racchiude e sintetizza le qualità della Secure Online Desktop , il suo AD Ing. Piergiorgio Venuti, professionista impagabile , sia dal punto di vista tecnico/organizzativo che soprattutto (e non dimeno) come persona , capace di gestire , risolvere e approcciare qualsivoglia attività/problematica, davvero un grande !!!!



Tempi veloci e staff preparato!
Ottima azienda, servizi molto utili, staff qualificato e competente. Raccomandata!read more
Ottimo supportoread more
E' un piacere poter collaborare con realtà di questo tiporead more
Un ottimo fornitore.
Io personalmente ho parlato con l' Ing. Venuti, valore aggiunto indubbiamente.read more

About
© 2024 Cyberfero s.r.l. All Rights Reserved. Sede Legale: via Statuto 3 - 42121 Reggio Emilia (RE) – PEC [email protected] Cod. fiscale e P.IVA 03058120357 – R.E.A. 356650 Informativa Privacy - Certificazioni ISO