

 Piergiorgio Venuti
Application programming interface: our User API
In the IT development process, sooner or later we come across API services, which stands for Application Programming Interface. To date it is impossible to imagine IT development without. With the API it is possible to connect a service to an application and integrate it efficiently. Before introducing the specific APIs of the Cloud Server service, it is good to know broadly what an API is and why they are so used in computer science.
What is an API and how does it work?
An Application Programming Interface is like an open language, whose rules are shared by a certain service. By teaching the rules of language to an application, it can communicate with the service and access all the functions and data that are available.
Speaking a little more formal: the API is an interface that allows an app to interact with an external service through a set of commands. It is not necessary to know the internal logic of the service, just use a simple command and the service will return the requested data.
I want to propose an analogy that can be useful to understand this tool. When you enter a restaurant and talk to a waiter, you can order the dishes, ask questions on the menu, ask for the bill and so on. This person is like a filter that separates you from all the complications behind the scenes. You won’t have to worry about dishes, ovens, staff or food reserves. The waiter becomes the interface that allows you to take advantage of all the services, without having to worry about how a restaurant works. Here, the waiter can be interpreted as the API of the restaurant.
The specific command, the request (or call) method and the syntax to be used, are information described in the documentation of the service that offers the application programming interfaces.
Purposes
This powerful tool is now everywhere, so much so that often we do not even realize how many services we use via API. Mainly application programming interfaces are a great way to do one of the following:
Exchange of data
In the restaurant example, asking the waiter a question is like exchanging data. It would be like an answer to a question regarding the data made available.
Hide complex parts and perform operations
In the restaurant example, you don’t need to know how to cook a perfect lasagna, you will just order it. The request requires that the service provide a product, not simply raw data.
Extend functionality
For example, in mobile operating systems, widgets, which display useful information on the screen as part of the background, are used through APIs. The OS requires the app that provides the widget, all the information it needs to correctly show this functionality. This is also done via API.
Increase security
Since it is the OS that manages the authorizations for the use of the various hardware components, it is in charge of requesting the user for authorization to share a component. The SO is therefore responsible for the security and management of the data collected by the sensors of the mobile phone.
To learn more about the API topic, we share an explanation video from the Simply Explained channel.
Cyberfero User API
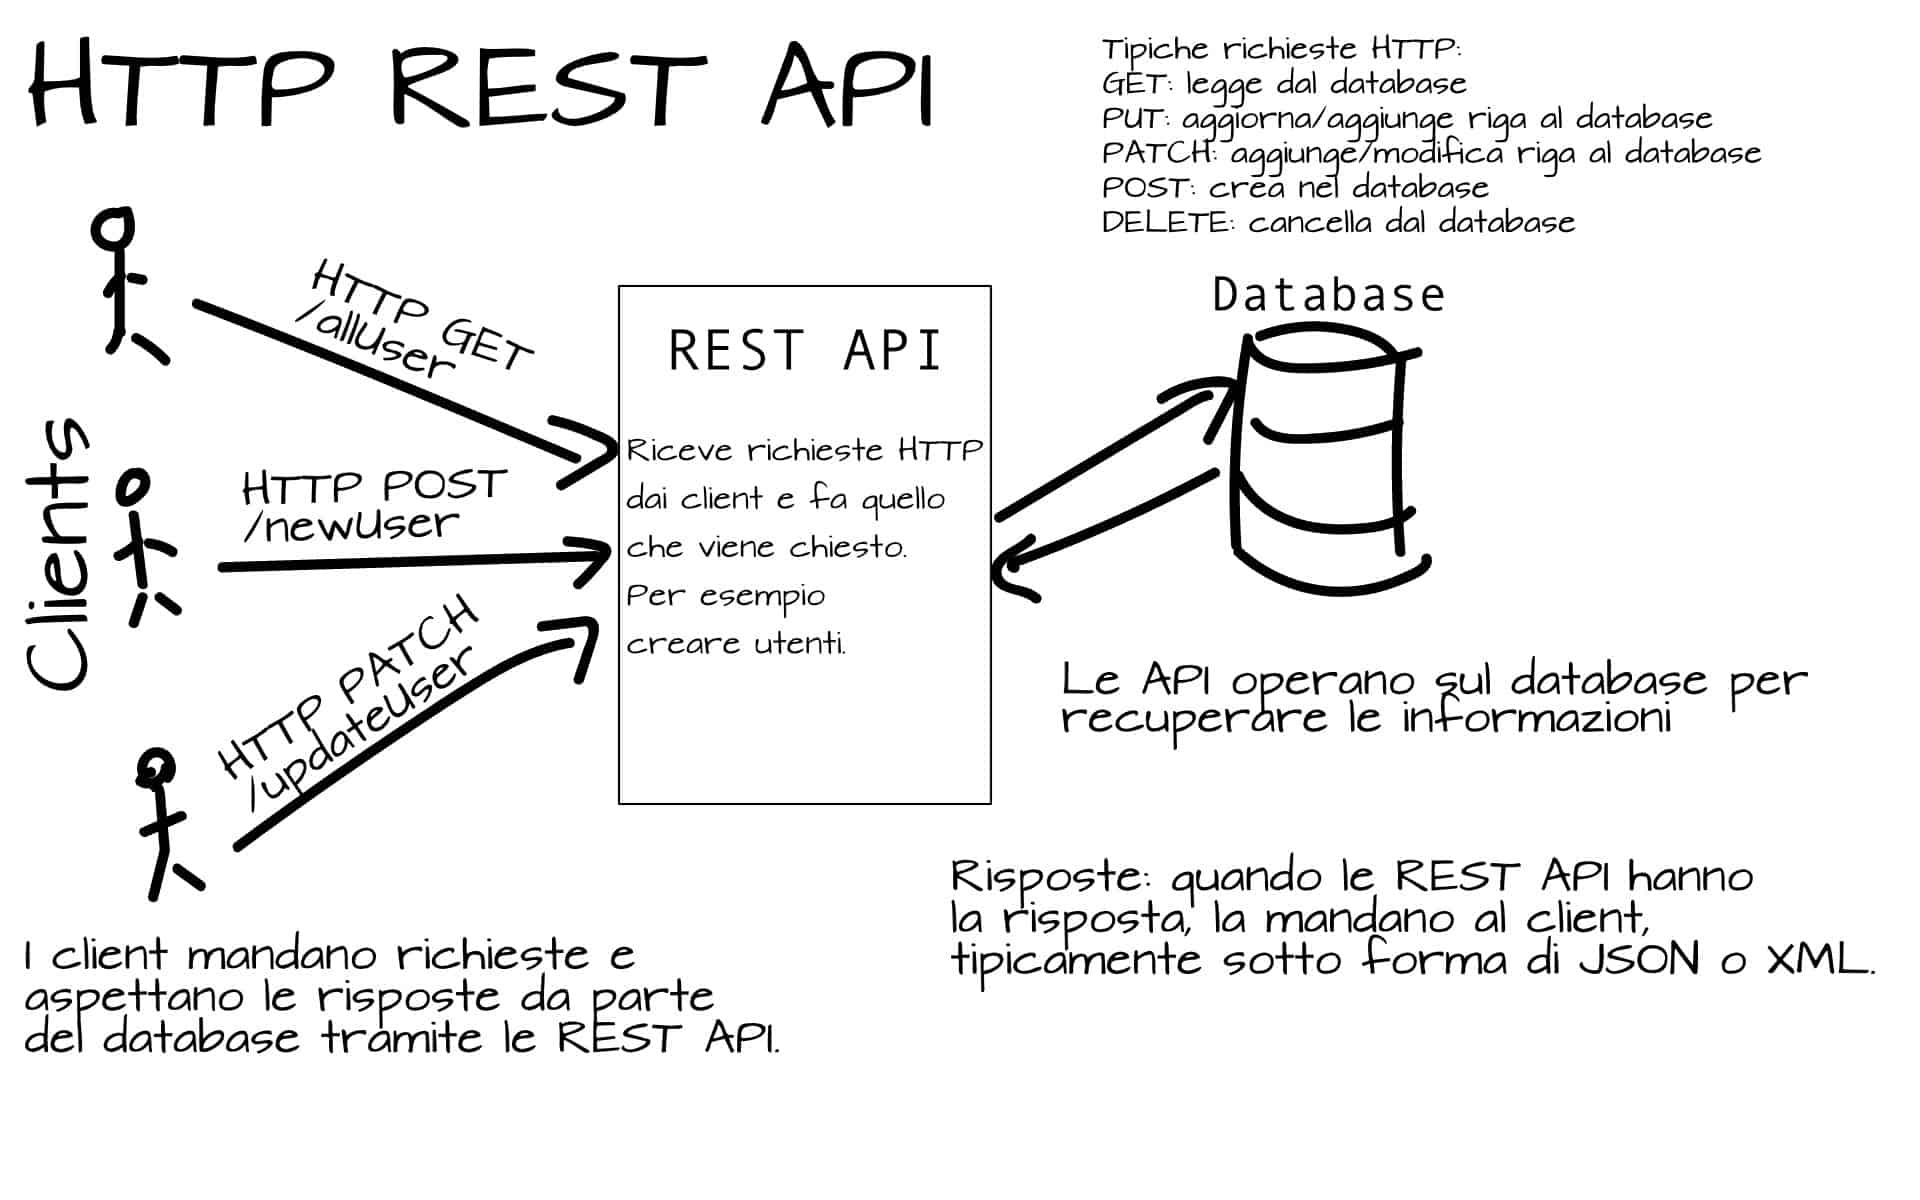
Cyberfero provides its User API to enable complete control of your account and services from your apps / systems. Through the HTTP REST API made available, it is also possible to resell the services with the white label formula, thus being able to brand the services in complete freedom.
HTTP REST API
This type of API is characterized by communication via HTTP protocol and compliance with architectural principles defined as REpresentational State Transfer. If the HTTP protocol and its communication methods are well known and widely understood, perhaps it is good to mention the REST principles.
In a university analysis published as a thesis by Roy Fielding, the principles for a software architecture that would allow us to see the Web as a distributed computing platform were analyzed. According to this analysis, which hypothesized a generic architecture, the Web was found to have all that is needed to be considered a perfect platform for distributed processing.
A set of API which respects the REST logic hypothesized in 2000 by Roy Fielding, is called RESTful API. Although the terms create confusion, in reality they perfectly reflect the concept that REST is not a technology or a language, but are simply guidelines that can be respected or not.
White Label
Our APIs are offered specifically to offer the possibility to our customers to offer our services in white label mode. This means that our services can be offered to the customers of our customers, without them realizing anything.
The practice of white label, in fact, consists precisely in offering products without brands, with the specific aim of encouraging the rebranding of the service. Another interesting advantage derived from the use of APIs.
Conclusions
In addition to the possibility of offering our services to your customers in white label, you can also use the API to implement the services directly in your apps, expanding the available development possibilities.
The APIs are offered with complete documentation of all the request methods offered. A multitude of different API calls are allowed including management of users, domains, DNS, virtual machines and much more.
Summarizing, through Cyberfero’s HTTP REST API it is possible:
1. implement access to virtual machines, hypervisors, network, disks, backups and much more in their applications
2. offer our re-branded services to your customers
Request further information or advice.
Useful links:
Share


RSS
More Articles…
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company
- NIS: what it is and how it protects cybersecurity
- Advanced persistent threats (APTs): what they are and how to defend yourself
- Penetration Testing and MFA: A Dual Strategy to Maximize Security
- Penetration Testing: Where to Strike to Protect Your IT Network
- Ransomware: a plague that brings companies and institutions to their knees. Should you pay the ransom? Here is the answer.
- Why IT audit and log management are important for Cybersecurity
- Red Team, Blue Team and Purple Team: what are the differences?
Categories …
- Backup as a Service (18)
- Acronis Cloud Backup (11)
- Veeam Cloud Connect (4)
- Cloud Conference (3)
- Cloud CRM (1)
- Cloud Server/VPS (22)
- Conferenza Cloud (4)
- Cyberfero (15)
- ICT Monitoring (5)
- Log Management (2)
- News (25)
- ownCloud (4)
- Privacy (7)
- Security (203)
- Cyber Threat Intelligence (CTI) (8)
- Deception (4)
- Ethical Phishing (11)
- Netwrix Auditor (2)
- Penetration Test (11)
- Posture Guard (3)
- SOCaaS (65)
- Vulnerabilities (84)
- Web Hosting (15)
Tags
 Unknown Feed
Full Disclosure
- Apache Struts2 Core Arbitrary Code Execution via OGNL Sandbox Escape November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below attempt to prevent arbitrary code execution via Object-Graph Navigation Language (OGNL) through several different mechanisms but only in a cursory fashion -- the libraries only guard against immediate calls evaluated by the OGNL engine via `SecurityMemberAccess`, but an allowed […]
- Apache Struts2 Core TokenHelper Token Cryptographic Timing Side-Channel November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Core 7.4.0 and below performs session token comparisons cryptographically insecure early-exit comparison functions (e.g., `!=`, `memcmp`, byte-by-byte loops with `break`) that return as soon as the first mismatched byte is encountered. The execution time of the comparison is therefore proportional to the number […]
- Apache Struts2 Spring Plugin Uses a Previously Closed Resource November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Spring Plugin opens a Spring `ApplicationContex` via a try-with-resources block and, outside of said block, then continues to use the closed resource, resulting in an uncaught `IllegalStateException`. This particular issue prevents proper functionality and indicates poor code quality and code review standards and […]
- Apache Struts2 Core Integer Overflow November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below fails to properly prevent integer overflows, causing wrap-arounds and other issues on a downstream forced casting into types smaller than `BigInteger`. Importantly, this finding underscores why all applications using Struts and other such platforms should perform their own input […]
- Apache Struts2 Core Cross-Origin Protection Exemption Miskeyed to a Deployment-Wide Path November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below's `FetchMetadataInterceptor`, `CoepInterceptor`, and `CoopInterceptor` each compare their `exemptedPaths` configuration -- a per-interceptor-reference, administrator-supplied set of paths intended to exempt specific actions from the corresponding cross-origin protection -- against `HttpServletRequest.getContextPath()`. `getContextPath()` is fixed for the entire deployed web...
- Apache Struts2 REST Plugin Fails to Properly Parse Chunked Requests November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 REST Plugin's (version 7.4.0 and below) `ContentTypeInterceptor.intercept(ActionInvocation)` only deserialises a request body and enforces the `struts.rest.content.maxLength` bound when `HttpServletRequest#getContentLength()` returns a positive value. `getContentLength()` returns `-1` whenever the `Content-Length` header is absent, which normal and appropriate for any Hypertext Transfer Protocol (HTTP)...
- Apache Struts2 REST Plugin Untrimmed `Accept` Header Tokens Break Content Negation Fallback November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 REST Plugin's `DefaultContentTypeHandlerManager.getHandlerForResponse(HttpServletRequest, HttpServletResponse)` splits the `Accept` header on commas and passes each resulting token directly to `findHandler(String)` without trimming leading or trailing whitespace. `findHandler(String)` only retries a trimmed lookup when a token contains a semicolon (`;`), so a token that merely carries […]
- Apache Struts2 JSON Plugin Insecure Deserialisation -- Object Deserialisation Element-Count Limit Bypass November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01As of the current versions of the Apache Struts2 JSON Plugin (e.g., version 7.4.0 and the 7.5.0 snapshot dated 28 October 2026), attackers can bypass the element-count limit purported to protect Object deserialisation added to said code as part of the WW-5618 and S2-072 "hardening controls". Please […]
- [0day-rubbish] NETGEAR RAX120 V1.2.5.18 authenticated SOAP InstallApp OS command injection to root-configured web-stack execution (6.8 Medium; conditionally 7.2 High with management exposure) October 29, 2026Posted by disclosure via Fulldisclosure on Oct 280day Rubbish Research Team is publicly disclosing a vulnerability in NETGEAR RAX120 (Nighthawk AX12) firmware V1.2.5.18, the WiFi 6 consumer router from NETGEAR (United States), built on the Qualcomm IPQ8074 platform. The administrative web plane of this firmware generation is a lighttpd server fronting the vendor's DNI-framework CGI […]
- [0day-rubbish] Raritan PX3 PDU G4 firmware 4.3.14 command injection in the ping and traceroute diagnostics through an inverted hostname-validation return check (8.8) October 29, 2026Posted by disclosure via Fulldisclosure on Oct 280day Rubbish Research Team is publicly disclosing a vulnerability in the Raritan PX3 PDU G4, firmware version 4.3.14, the intelligent rack power distribution unit from Raritan, a Legrand company (United States). A low-privilege authenticated session converts one diagnostics request into operating-system command execution in the product's web-service context, […]
Customers


Twitter FEED
Recent activity
-
SecureOnlineDesktop
Estimated reading time: 6 minutes L'impatto crescente delle minacce informatiche, su sistemi operativi privati op… https://t.co/FimxTS4o9G
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The growing impact of cyber threats, on private or corporate operating systems… https://t.co/y6G6RYA9n1
-
SecureOnlineDesktop
Tempo di lettura stimato: 6 minuti Today we are talking about the CTI update of our services. Data security is… https://t.co/YAZkn7iFqa
-
SecureOnlineDesktop
Estimated reading time: 6 minutes Il tema della sicurezza delle informazioni è di grande attualità in questo peri… https://t.co/tfve5Kzr09
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The issue of information security is very topical in this historical period ch… https://t.co/TP8gvdRcrF
Newsletter
Products and Solutions
Partners
Cloud Models
News
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company May 6, 2024
- NIS: what it is and how it protects cybersecurity April 22, 2024
- Advanced persistent threats (APTs): what they are and how to defend yourself April 17, 2024
- Penetration Testing and MFA: A Dual Strategy to Maximize Security April 15, 2024
- Penetration Testing: Where to Strike to Protect Your IT Network March 25, 2024
Google Reviews



Ottima azienda, servizi molto utili, staff qualificato e competente. Raccomandata!read more
Ottimo supportoread more
E'... un piacere poter collaborare con realtà di questo tiporead more
Un ottimo fornitore.
Io personalmente ho parlato con l' Ing. Venuti, valore aggiunto indubbiamente.read more

About
© 2024 Cyberfero s.r.l. All Rights Reserved. Sede Legale: via Statuto 3 - 42121 Reggio Emilia (RE) – PEC [email protected] Cod. fiscale e P.IVA 03058120357 – R.E.A. 356650 Informativa Privacy - Certificazioni ISO