

 Piergiorgio Venuti
Cyber Threat Hunting: on the hunt for security threats
Estimated reading time: 5 minutes
Cyber Threat Hunting is a proactive security search across networks, endpoints and datasets to hunt down malicious, suspicious or risky activities that have escaped detection by existing tools.
Definition
There is a distinction between malware detection and cyber threat hunting . Threat detection is a passive approach to monitoring data and systems to identify potential security problems. However, it is a necessity and can help a threat hunter . Instead, proactive threat hunting tactics have evolved to use new threat intelligence on previously collected data to identify and classify potential risks before the attack .
Security personnel cannot afford to believe that their security system is impenetrable. Must always remain vigilant for the next threat or vulnerability . Rather than sitting around and waiting for threats to strike, cyber threat hunting develops hypotheses based on knowing the behaviors of threat actors and validating those hypotheses through active research in the environment .
With threat hunting, an expert doesn’t start with an alarm or indicators of compromise (IOC), but with deeper reasoning. In many cases the threat hunter’s efforts create and concretize the alarm or the IOC.
This aggressively assumes that a breach has occurred or will occur at the company. Security officers hunt down threats in their environment rather than rely on automatisms.
Threat hunting practice
For companies that are ready to take a more proactive approach to cybersecurity , which tries to stop attacks before they get too deep, adding threat hunting protocols to their security program is the next logical step.
After consolidating endpoint security and incident response strategies to mitigate the now unavoidable known malware attacks, companies can begin to take the offensive . This means digging deep and finding what hasn’t been detected yet. This is precisely the purpose of cyber threat hunting.
As mentioned earlier, threat hunting is an aggressive tactic that starts from the premise of the “assumption of violation”. Attackers are already inside an organization’s network and are secretly monitoring and moving into it.
This may sound far-fetched, but in reality, attackers can be inside a network for days, weeks, and even months . In the meantime, they prepare and execute attacks as advanced persistent threats, with no automatic defense detecting their presence . Cyber threat hunting stops these attacks by looking for covert indicators of compromise (IOCs) so they can be mitigated before the attacks reach their goals.
The key elements of a threat hunting
The goal of the threat hunt is to monitor daily activities and traffic across the network and investigate possible anomalies to find any undiscovered malicious activity that could lead to a complete breach . To achieve this level of proactive detection, threat hunting incorporates four equally important components.
1. Methodology
To be successful in hunt for threats, companies must commit to a proactive, full-time approach that is continuous and evolving. Instead, a responsive, ad hoc implementation, “ when we have time “, will be self-defeating and will only lead to minimal results.
2. Technology
Most companies already have comprehensive endpoint security solutions with automatic detection. Threat hunting works in addition to these and adds advanced technologies . The aim is to find anomalies, unusual patterns, and other traces of attackers that shouldn’t be in systems and files.
The new cloud-native endpoint protection (EPP) platforms that leverage big data analytics can capture and analyze large volumes of non-data filtered on endpoints, while behavioral analytics and artificial intelligence can provide broad, high-speed visibility into malicious behaviors that seem normal at first.
3. Highly qualified and dedicated staff
The threat hunters are a race of their own. These experts know how to use the security technology deployed by companies. In addition, also combine the aspiration to go on the offensive with intuitive problem-solving skills to uncover and mitigate hidden threats.
4. Threat intelligence
Having access to evidence-based global intelligence from experts from around the world (e.g. Miter Att & amp; ck ) further improves and accelerates hunting for existing threats. Hunters are aided by information such as attack classifications for identifying malware and threat groups , as well as advanced threat indicators.
The abilities of a threat hunter
The Threat Hunting Report from Crowd Research Partners confirms the importance of certain capabilities for threat hunting. When asked to rank the most important skill, the survey found that:
69% chose threat intelligence
57% chose behavior analysis
56% chose automatic detection
54% chose machine learning and automated analysis
The profile of a threat hunter
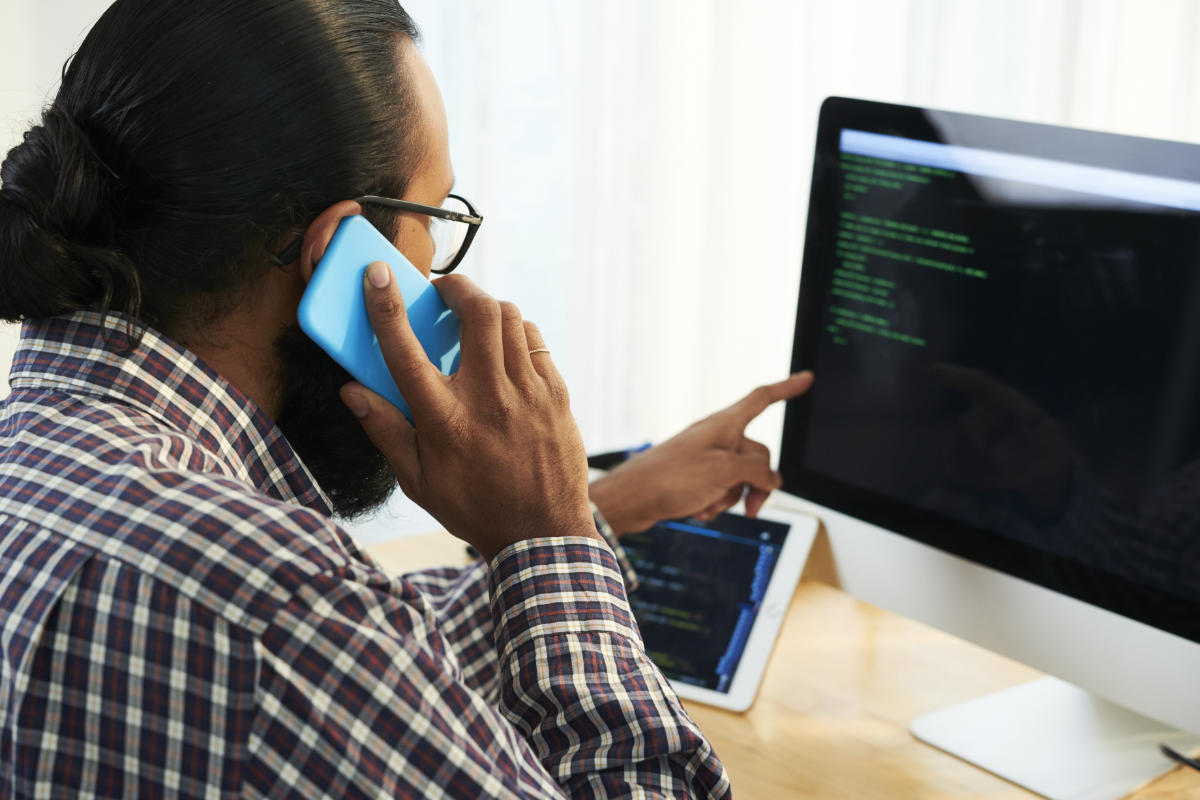
Threat hunters look for attackers who manage to break through vulnerabilities that a company might not even know exist . These attackers spend a considerable amount of time planning and performing the reconnaissance, acting only when they know they can successfully penetrate the network without warning. They also inject and build malware that has not yet been recognized or use techniques that do not rely on malware at all, to provide a persistent base from which to attack.
What does it take to outsmart even the smartest attackers?
A cyber threat hunter is relentless and can find even the smallest trace of what attackers have left behind. In general, threat hunters use their skills to undo the small changes that occur when attackers make their moves within a system or file.
The best threat hunters rely on their instincts to sniff out the stealth moves of the most dangerous attacker.
Are you a threat hunter? Contact us!
Cyberfero is looking for a SOC / ICT analyst to add to the team. If you think you’re the right person, visit this page to view the detailed job posting.
Useful links:
Cyber Threat Intelligence (CTI) – greater effectiveness for IT security
Share


RSS
More Articles…
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company
- NIS: what it is and how it protects cybersecurity
- Advanced persistent threats (APTs): what they are and how to defend yourself
- Penetration Testing and MFA: A Dual Strategy to Maximize Security
- Penetration Testing: Where to Strike to Protect Your IT Network
- Ransomware: a plague that brings companies and institutions to their knees. Should you pay the ransom? Here is the answer.
- Why IT audit and log management are important for Cybersecurity
- Red Team, Blue Team and Purple Team: what are the differences?
Categories …
- Backup as a Service (18)
- Acronis Cloud Backup (11)
- Veeam Cloud Connect (4)
- Cloud Conference (3)
- Cloud CRM (1)
- Cloud Server/VPS (22)
- Conferenza Cloud (4)
- Cyberfero (15)
- ICT Monitoring (5)
- Log Management (2)
- News (25)
- ownCloud (4)
- Privacy (7)
- Security (203)
- Cyber Threat Intelligence (CTI) (8)
- Deception (4)
- Ethical Phishing (11)
- Netwrix Auditor (2)
- Penetration Test (11)
- Posture Guard (3)
- SOCaaS (65)
- Vulnerabilities (84)
- Web Hosting (15)
Tags
 Unknown Feed
Full Disclosure
- SEC Consult SA-20261104-0 :: Improper device certificate validation enables AiTM attacks in Siemens SICAM Toolbox II device communication November 5, 2026Posted by SEC Consult Vulnerability Lab via Fulldisclosure on Nov 04SEC Consult Vulnerability Lab Security Advisory < 20261104-0 > ======================================================================= title: Improper device certificate validation enables AiTM attacks product: Siemens SICAM Toolbox II device communication vulnerable version:
- Apache Struts2 Tiles Plugin <=7.4.0 and >=6.3.0 Preparer Cache Vulnerabilities November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04The Apache Struts2 Tiles plugin version =6.3.0) codebase includes a `ViewPreparer` construct, replete with multiple ViewPreparer factories, that contains several important vulnerabilities including unsynchronised, unbounded caches. The lack of proper synchronisation means that certain factories will create caches that race, risking lost cache entries, corrupted internal bucket […]
- unixODBC <=2.3.14 Rude Truncation via Narrowing Conversion Causes Out-of-Bounds `memcpy` November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04unixODBC versions
- unixODBC <=2.3.14 Multiple Races November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04The unixODBC driver manager library contains multiple races of importance / interest, including a set of data races in the connection-pooling configuration state data that can cause one thread to read a half-written pool-size or timeout value, which can lead to a variety of harmful effects, as […]
- unixODBC <=2.3.14 Multiple Heap Buffer Overflows, Underflows, and Over-Reads November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04unixODBC versions 2.3.14 and below contain multiple heap buffer overflows, underflows, and over-reads. Attackers who can influence various arguments passed thereto can trigger the heap-based buffer overflows inside of the unixODBC driver manager itself, potentially corrupting the shared heap state across connections, crash the driver manager (thereby […]
- Apache Struts2 Core Arbitrary Code Execution via OGNL Sandbox Escape November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below attempt to prevent arbitrary code execution via Object-Graph Navigation Language (OGNL) through several different mechanisms but only in a cursory fashion -- the libraries only guard against immediate calls evaluated by the OGNL engine via `SecurityMemberAccess`, but an allowed […]
- Apache Struts2 Core TokenHelper Token Cryptographic Timing Side-Channel November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Core 7.4.0 and below performs session token comparisons cryptographically insecure early-exit comparison functions (e.g., `!=`, `memcmp`, byte-by-byte loops with `break`) that return as soon as the first mismatched byte is encountered. The execution time of the comparison is therefore proportional to the number […]
- Apache Struts2 Spring Plugin Uses a Previously Closed Resource November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Spring Plugin opens a Spring `ApplicationContex` via a try-with-resources block and, outside of said block, then continues to use the closed resource, resulting in an uncaught `IllegalStateException`. This particular issue prevents proper functionality and indicates poor code quality and code review standards and […]
- Apache Struts2 Core Integer Overflow November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below fails to properly prevent integer overflows, causing wrap-arounds and other issues on a downstream forced casting into types smaller than `BigInteger`. Importantly, this finding underscores why all applications using Struts and other such platforms should perform their own input […]
- Apache Struts2 Core Cross-Origin Protection Exemption Miskeyed to a Deployment-Wide Path November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below's `FetchMetadataInterceptor`, `CoepInterceptor`, and `CoopInterceptor` each compare their `exemptedPaths` configuration -- a per-interceptor-reference, administrator-supplied set of paths intended to exempt specific actions from the corresponding cross-origin protection -- against `HttpServletRequest.getContextPath()`. `getContextPath()` is fixed for the entire deployed web...
Customers


Twitter FEED
Recent activity
-
SecureOnlineDesktop
Estimated reading time: 6 minutes L'impatto crescente delle minacce informatiche, su sistemi operativi privati op… https://t.co/FimxTS4o9G
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The growing impact of cyber threats, on private or corporate operating systems… https://t.co/y6G6RYA9n1
-
SecureOnlineDesktop
Tempo di lettura stimato: 6 minuti Today we are talking about the CTI update of our services. Data security is… https://t.co/YAZkn7iFqa
-
SecureOnlineDesktop
Estimated reading time: 6 minutes Il tema della sicurezza delle informazioni è di grande attualità in questo peri… https://t.co/tfve5Kzr09
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The issue of information security is very topical in this historical period ch… https://t.co/TP8gvdRcrF
Newsletter
Products and Solutions
Partners
Cloud Models
News
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company May 6, 2024
- NIS: what it is and how it protects cybersecurity April 22, 2024
- Advanced persistent threats (APTs): what they are and how to defend yourself April 17, 2024
- Penetration Testing and MFA: A Dual Strategy to Maximize Security April 15, 2024
- Penetration Testing: Where to Strike to Protect Your IT Network March 25, 2024
Google Reviews



Ottima azienda, servizi molto utili, staff qualificato e competente. Raccomandata!read more
Ottimo supportoread more
E'... un piacere poter collaborare con realtà di questo tiporead more
Un ottimo fornitore.
Io personalmente ho parlato con l' Ing. Venuti, valore aggiunto indubbiamente.read more

About
© 2024 Cyberfero s.r.l. All Rights Reserved. Sede Legale: via Statuto 3 - 42121 Reggio Emilia (RE) – PEC [email protected] Cod. fiscale e P.IVA 03058120357 – R.E.A. 356650 Informativa Privacy - Certificazioni ISO