

 Alessandro Stesi
Subscription business model – Basics
subscription
Subscription is a convenient way to receive updates, products or services on a regular and ongoing basis. This business model has stood the test of time. Over the years, satisfied customers have used regular services by subscribing news, magazines, CDs, wine and even opera tickets. And then the cloud arrived. The cloud has made IT complex easy and cheap, thanks to the familiar service delivery subscription model.
Today, public cloud computing services have revenues of $ 246.8 billion. By 2020, Gartner says, cloud adoption strategies will affect over 50% of IT outsourcing contracts. Service providers are rushing to get on board.
Subscription
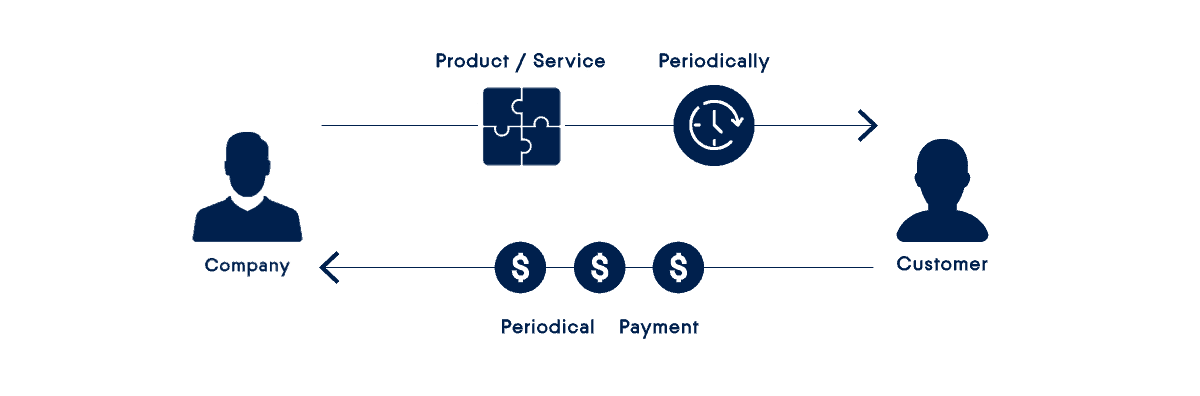
The subscription is an agreement to regularly receive products or services by paying in advance. It has become a default business model for service providers. Even those service integrators who have made their name by selling individual software licenses are currently switching to a subscription or a software-as-a-service service delivery method to stay alive and grow their customer base.
For customers, the subscription is based on practicality, scalability and economy. The consumption model of the OpEx-based subscription service beats the traditional CapEx model in all ways. Instead of spending hundreds and often thousands of euros on hardware devices and software licenses (and therefore worry about maintenance and upgrades), companies pay a manageable monthly fee just for what they use and only for the service they need.
Subscription models
There are two popular subscription models designed to attract new customers allowing them to try the service before engaging in a full subscription.
Freemium
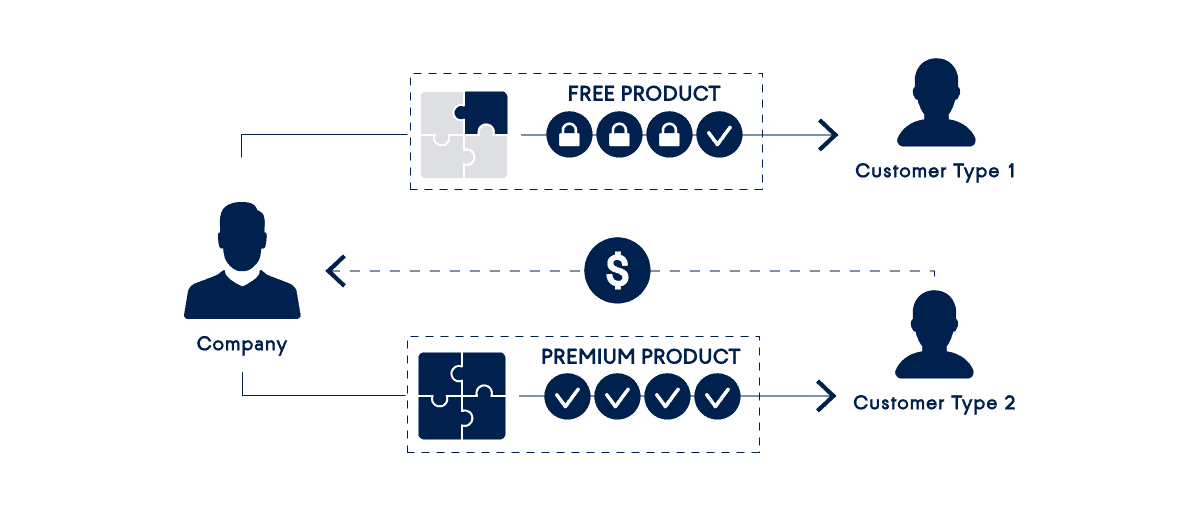
A freemium business model offers a free basic service and additional paid features. This has become one of the dominant business models in the mobile app market and is widely adopted by cloud-based service providers. LinkedIn, Dropbox, Yammer and millions of other vendors have adopted this model, using free features as a powerful marketing tool. Users are more likely to direct the service to others when it’s free and easy to use. There are also signs that the freemium model is even more successful than the 30-day trial because it relieves customers from the cumbersome cancellation process when they are trying out the service for the first time.
As with the Acronis Cloud Backup service, the Freemium option allows you to have a free plan for a computer with local backup storage and then charge a fee for additional services such as cloud storage and other devices.
Bait and Hook
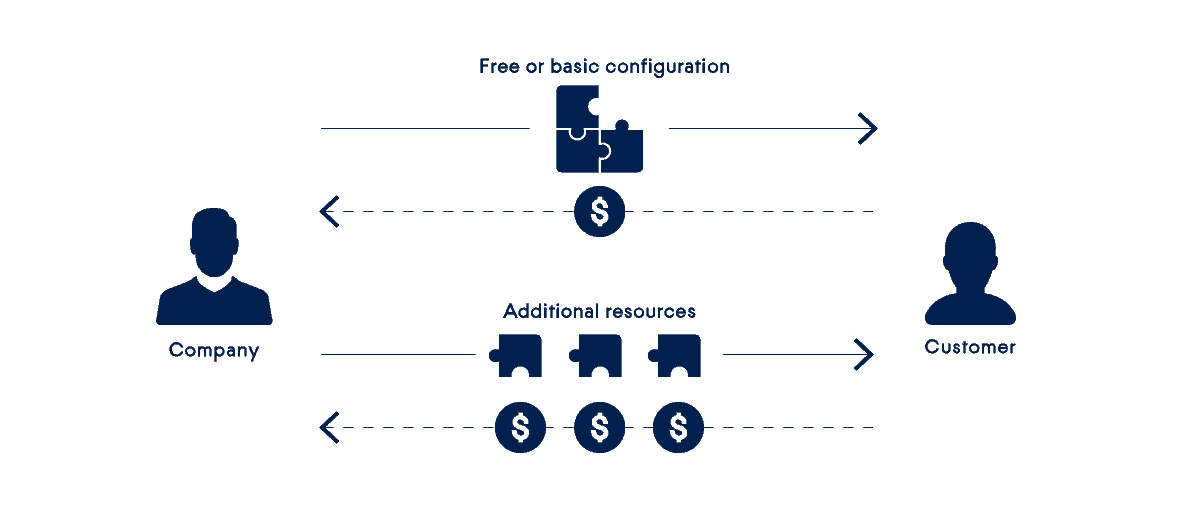
This subscription business model offers to offer a basic service at a low price, or even free, and to charge the full price for additional resources. The origin of this subscription method is often attributed to Gillette, a razor company that is known for selling cheap razor kits and expensive blade refills. Today this model is widely used by mobile phone companies (free telephone with a long-term service plan), printer manufacturers (cheap printers, expensive ink) and many other companies where most of the revenue comes from consumables .
With the Acronis Cloud Backup service, on the other hand, you have a free plan with a limited amount of storage space in the Cloud. This will allow customers to register and try the fully functional service before purchasing additional Cloud storage to meet their needs. In this section you can consult the complete list of demo services that Cyberfero makes available to its customers.
Acronis Cloud Backup
The Acronis Cloud Backup service is specifically designed to meet the ever-increasing needs of customers oriented to the above-mentioned subscription models.
[btnsx id=”2931″]
Useful links:
A Hybrid Cloud Backup Solution for System Integrator and reseller
BaaS | Cloud Backup | Backup as a Service
New Acronis Cloud Backup model for end users and new reseller plan
Share


RSS
More Articles…
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company
- NIS: what it is and how it protects cybersecurity
- Advanced persistent threats (APTs): what they are and how to defend yourself
- Penetration Testing and MFA: A Dual Strategy to Maximize Security
- Penetration Testing: Where to Strike to Protect Your IT Network
- Ransomware: a plague that brings companies and institutions to their knees. Should you pay the ransom? Here is the answer.
- Why IT audit and log management are important for Cybersecurity
- Red Team, Blue Team and Purple Team: what are the differences?
Categories …
- Backup as a Service (18)
- Acronis Cloud Backup (11)
- Veeam Cloud Connect (4)
- Cloud Conference (3)
- Cloud CRM (1)
- Cloud Server/VPS (22)
- Conferenza Cloud (4)
- Cyberfero (15)
- ICT Monitoring (5)
- Log Management (2)
- News (25)
- ownCloud (4)
- Privacy (7)
- Security (203)
- Cyber Threat Intelligence (CTI) (8)
- Deception (4)
- Ethical Phishing (11)
- Netwrix Auditor (2)
- Penetration Test (11)
- Posture Guard (3)
- SOCaaS (65)
- Vulnerabilities (84)
- Web Hosting (15)
Tags
 Unknown Feed
Full Disclosure
- SEC Consult SA-20261104-0 :: Improper device certificate validation enables AiTM attacks in Siemens SICAM Toolbox II device communication November 5, 2026Posted by SEC Consult Vulnerability Lab via Fulldisclosure on Nov 04SEC Consult Vulnerability Lab Security Advisory < 20261104-0 > ======================================================================= title: Improper device certificate validation enables AiTM attacks product: Siemens SICAM Toolbox II device communication vulnerable version:
- Apache Struts2 Tiles Plugin <=7.4.0 and >=6.3.0 Preparer Cache Vulnerabilities November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04The Apache Struts2 Tiles plugin version =6.3.0) codebase includes a `ViewPreparer` construct, replete with multiple ViewPreparer factories, that contains several important vulnerabilities including unsynchronised, unbounded caches. The lack of proper synchronisation means that certain factories will create caches that race, risking lost cache entries, corrupted internal bucket […]
- unixODBC <=2.3.14 Rude Truncation via Narrowing Conversion Causes Out-of-Bounds `memcpy` November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04unixODBC versions
- unixODBC <=2.3.14 Multiple Races November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04The unixODBC driver manager library contains multiple races of importance / interest, including a set of data races in the connection-pooling configuration state data that can cause one thread to read a half-written pool-size or timeout value, which can lead to a variety of harmful effects, as […]
- unixODBC <=2.3.14 Multiple Heap Buffer Overflows, Underflows, and Over-Reads November 5, 2026Posted by Daniel Owens via Fulldisclosure on Nov 04unixODBC versions 2.3.14 and below contain multiple heap buffer overflows, underflows, and over-reads. Attackers who can influence various arguments passed thereto can trigger the heap-based buffer overflows inside of the unixODBC driver manager itself, potentially corrupting the shared heap state across connections, crash the driver manager (thereby […]
- Apache Struts2 Core Arbitrary Code Execution via OGNL Sandbox Escape November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below attempt to prevent arbitrary code execution via Object-Graph Navigation Language (OGNL) through several different mechanisms but only in a cursory fashion -- the libraries only guard against immediate calls evaluated by the OGNL engine via `SecurityMemberAccess`, but an allowed […]
- Apache Struts2 Core TokenHelper Token Cryptographic Timing Side-Channel November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Core 7.4.0 and below performs session token comparisons cryptographically insecure early-exit comparison functions (e.g., `!=`, `memcmp`, byte-by-byte loops with `break`) that return as soon as the first mismatched byte is encountered. The execution time of the comparison is therefore proportional to the number […]
- Apache Struts2 Spring Plugin Uses a Previously Closed Resource November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description The Apache Struts2 Spring Plugin opens a Spring `ApplicationContex` via a try-with-resources block and, outside of said block, then continues to use the closed resource, resulting in an uncaught `IllegalStateException`. This particular issue prevents proper functionality and indicates poor code quality and code review standards and […]
- Apache Struts2 Core Integer Overflow November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below fails to properly prevent integer overflows, causing wrap-arounds and other issues on a downstream forced casting into types smaller than `BigInteger`. Importantly, this finding underscores why all applications using Struts and other such platforms should perform their own input […]
- Apache Struts2 Core Cross-Origin Protection Exemption Miskeyed to a Deployment-Wide Path November 2, 2026Posted by Daniel Owens via Fulldisclosure on Nov 01Description Apache Struts2 Core version 7.4.0 and below's `FetchMetadataInterceptor`, `CoepInterceptor`, and `CoopInterceptor` each compare their `exemptedPaths` configuration -- a per-interceptor-reference, administrator-supplied set of paths intended to exempt specific actions from the corresponding cross-origin protection -- against `HttpServletRequest.getContextPath()`. `getContextPath()` is fixed for the entire deployed web...
Customers






Twitter FEED
Recent activity
-
SecureOnlineDesktop
Estimated reading time: 6 minutes L'impatto crescente delle minacce informatiche, su sistemi operativi privati op… https://t.co/FimxTS4o9G
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The growing impact of cyber threats, on private or corporate operating systems… https://t.co/y6G6RYA9n1
-
SecureOnlineDesktop
Tempo di lettura stimato: 6 minuti Today we are talking about the CTI update of our services. Data security is… https://t.co/YAZkn7iFqa
-
SecureOnlineDesktop
Estimated reading time: 6 minutes Il tema della sicurezza delle informazioni è di grande attualità in questo peri… https://t.co/tfve5Kzr09
-
SecureOnlineDesktop
Estimated reading time: 6 minutes The issue of information security is very topical in this historical period ch… https://t.co/TP8gvdRcrF
Newsletter
Products and Solutions
Partners
Cloud Models
News
- From Cyberfero to Cyberfero: rebranding of the leading cybersecurity company May 6, 2024
- NIS: what it is and how it protects cybersecurity April 22, 2024
- Advanced persistent threats (APTs): what they are and how to defend yourself April 17, 2024
- Penetration Testing and MFA: A Dual Strategy to Maximize Security April 15, 2024
- Penetration Testing: Where to Strike to Protect Your IT Network March 25, 2024
Google Reviews




Ottima azienda, servizi molto utili, staff qualificato e competente. Raccomandata!read more
Ottimo supportoread more
E'... un piacere poter collaborare con realtà di questo tiporead more
Un ottimo fornitore.
Io personalmente ho parlato con l' Ing. Venuti, valore aggiunto indubbiamente.read more


About
© 2024 Cyberfero s.r.l. All Rights Reserved. Sede Legale: via Statuto 3 - 42121 Reggio Emilia (RE) – PEC [email protected] Cod. fiscale e P.IVA 03058120357 – R.E.A. 356650 Informativa Privacy - Certificazioni ISO